Data Security
Stealing PII: Attack Paths, Detection, and Response
Understand how attackers steal PII through identity, endpoint, cloud, SaaS, email, database, and insider paths, and how to detect, contain, and scope it.
Guidance and practical considerations for incident response.
6 resources
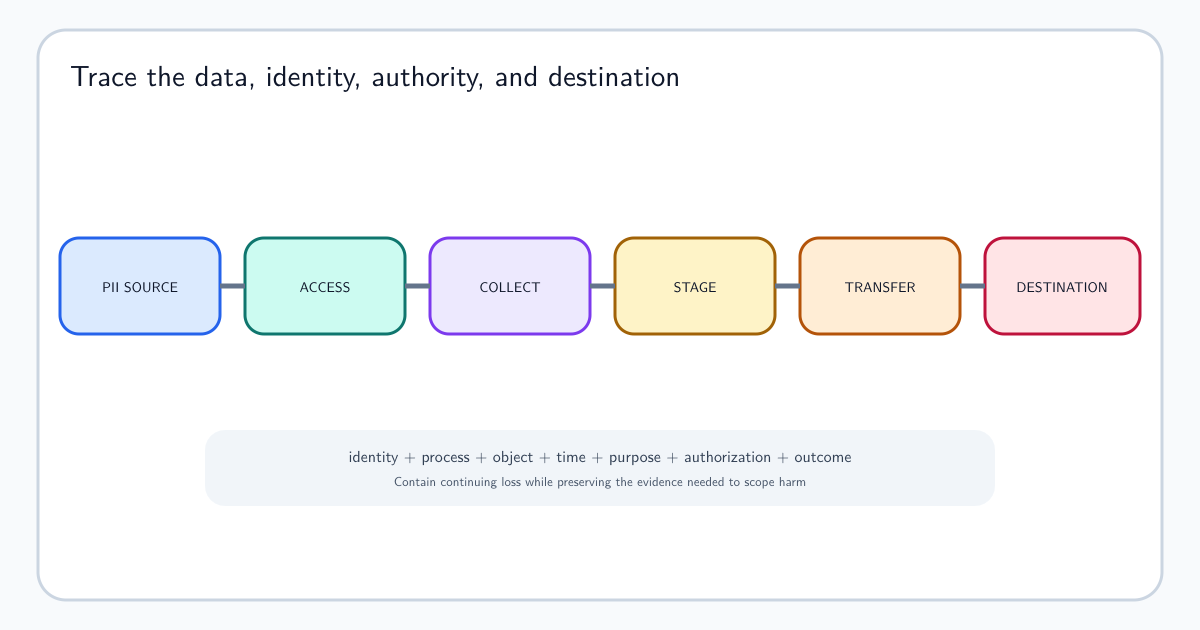
Understand how attackers steal PII through identity, endpoint, cloud, SaaS, email, database, and insider paths, and how to detect, contain, and scope it.
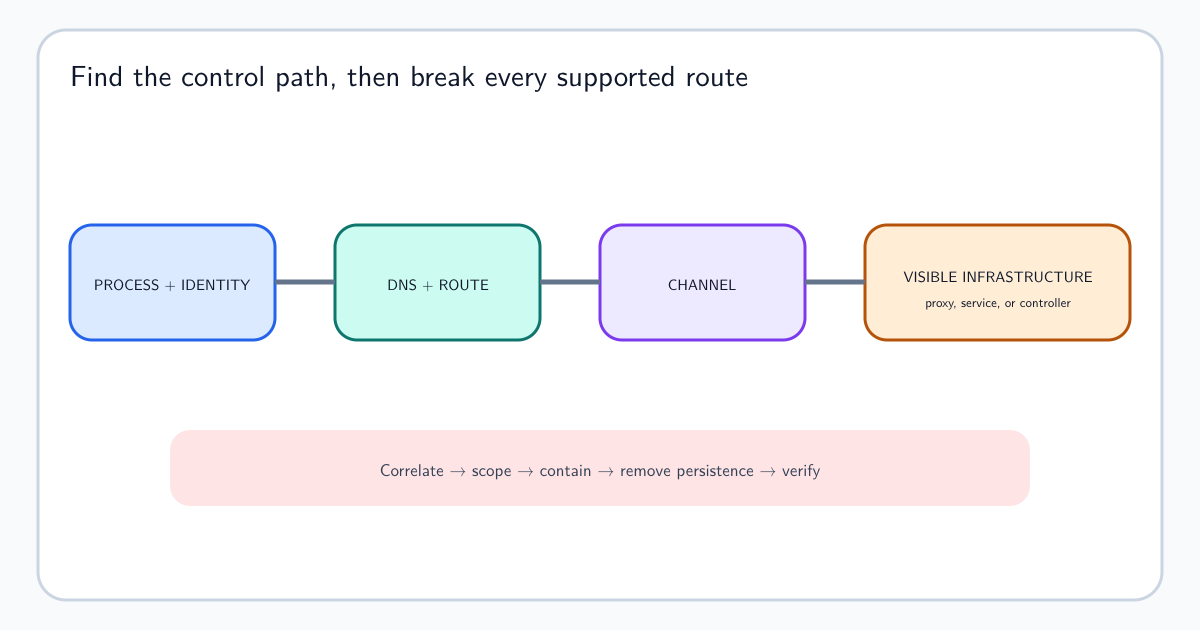
Learn how command-and-control channels work, which evidence reveals C2 activity, how to investigate it, and how to contain access without losing scope.
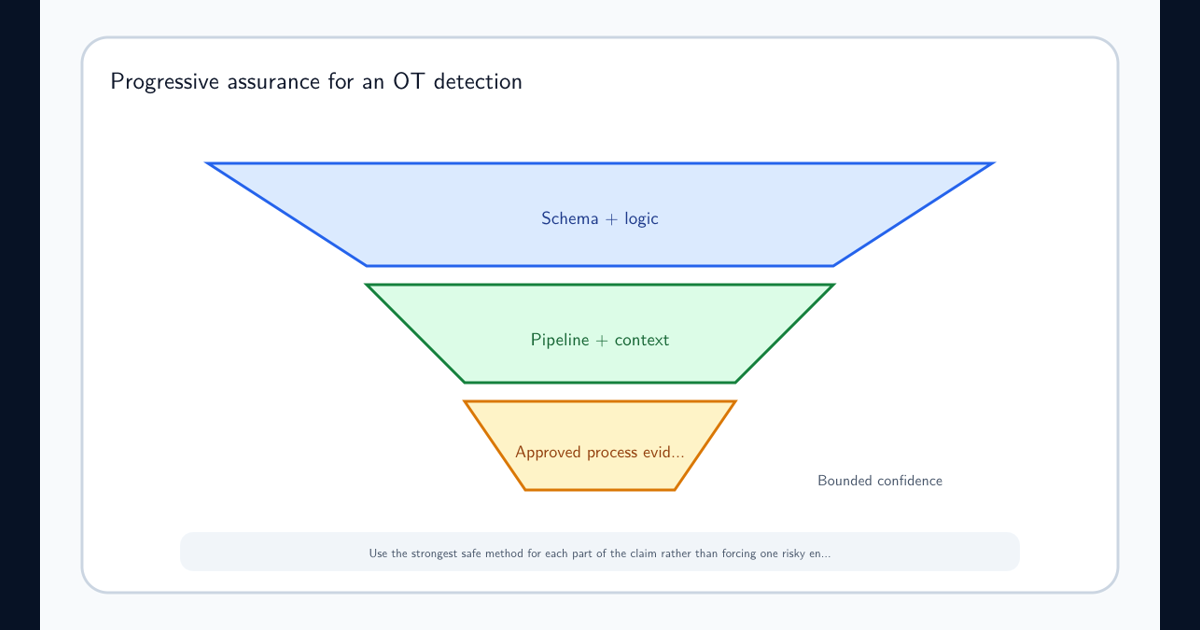
Build confidence in OT detections through progressively stronger, process-approved evidence while keeping validation and response from creating the physical harm they are meant to prevent.
Learn how sessions are created, stolen, replayed, detected, revoked, and investigated across browsers and cloud services.
Follow an evidence-led incident response lifecycle from preparation and triage through recovery and durable improvement.
Decide whether a security question belongs to Cyber Threat Intelligence, incident response, or a joint workflow—and design the handoffs that turn external context and incident evidence int...