Incident Response
Inhibit System Recovery: Ransomware Detection Guide
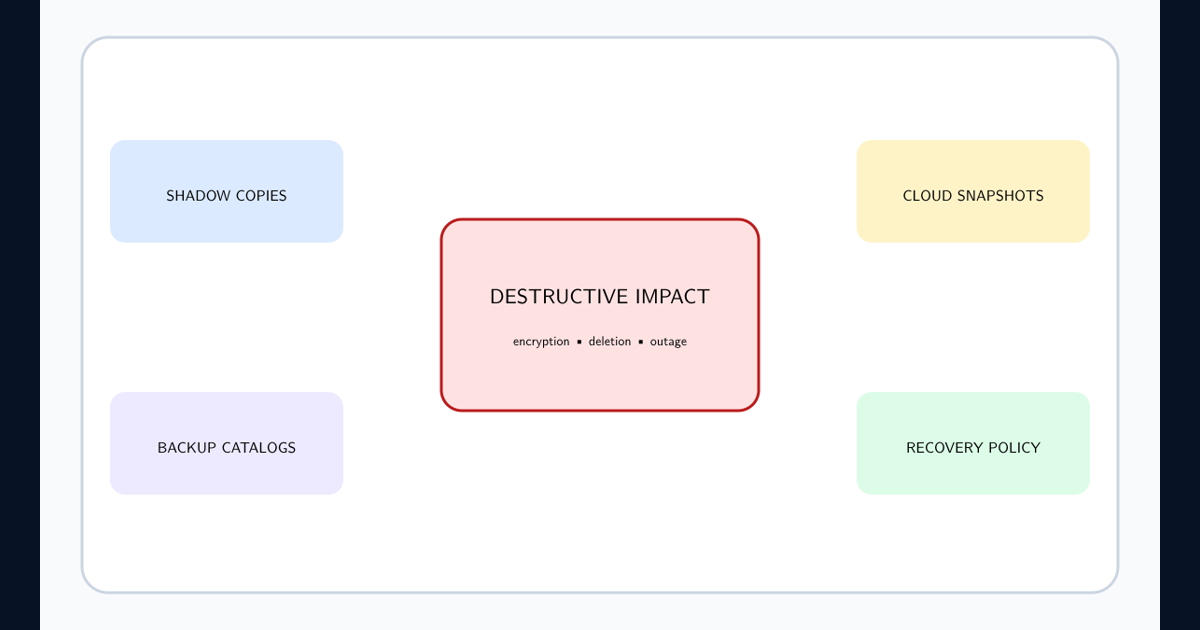
Inhibit system recovery detection covers shadow-copy deletion, backup-catalog changes, recovery disablement, cloud snapshot removal, and containment.
Practical guidance for incident response decisions and defensible security work.
8 resources
Inhibit system recovery detection covers shadow-copy deletion, backup-catalog changes, recovery disablement, cloud snapshot removal, and containment.
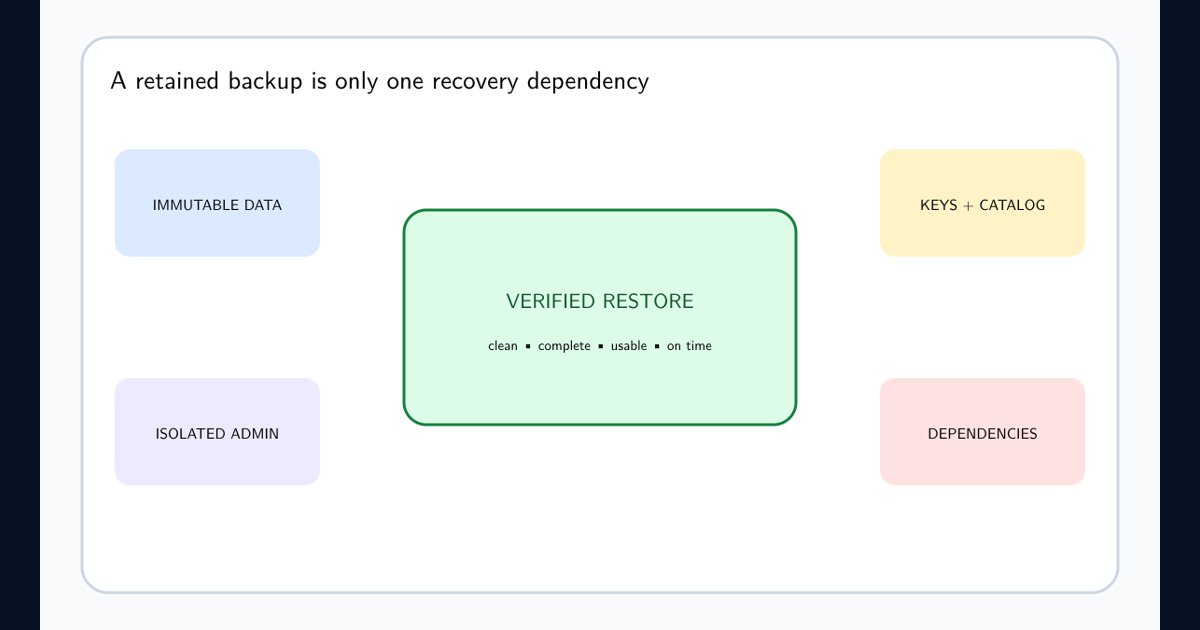
Immutable backup ransomware recovery requires isolated administration, retention locks, independent identities, clean restore points, and tested dependencies.
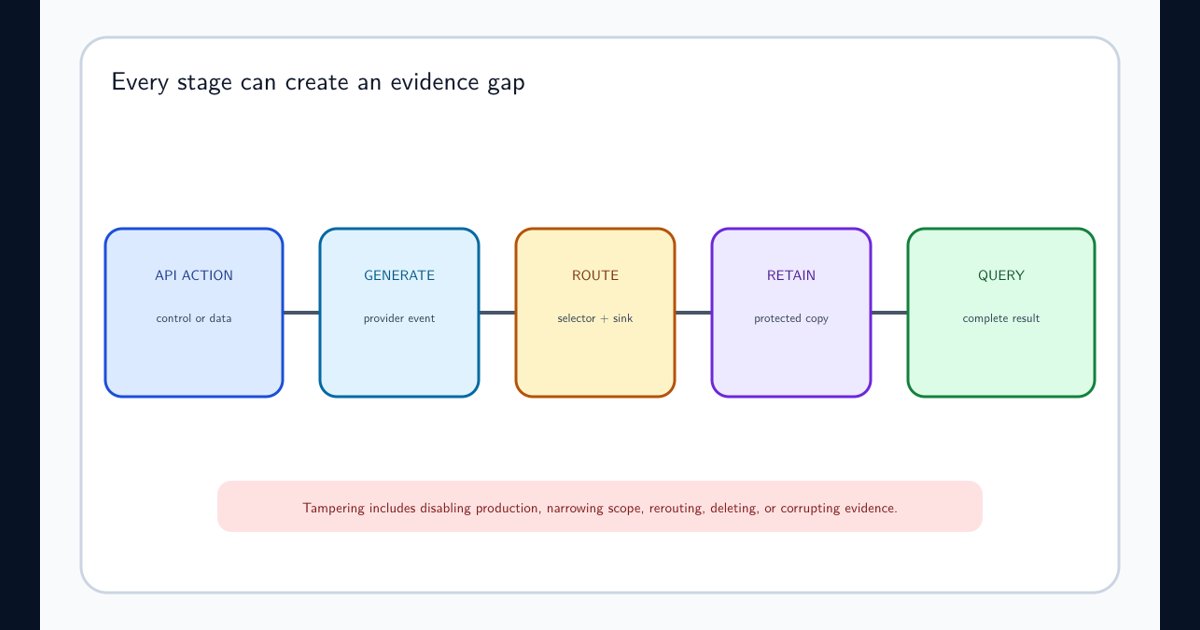
Cloud audit log tampering detection covers configuration changes, delivery gaps, integrity validation, immutable storage, independent evidence, and recovery.
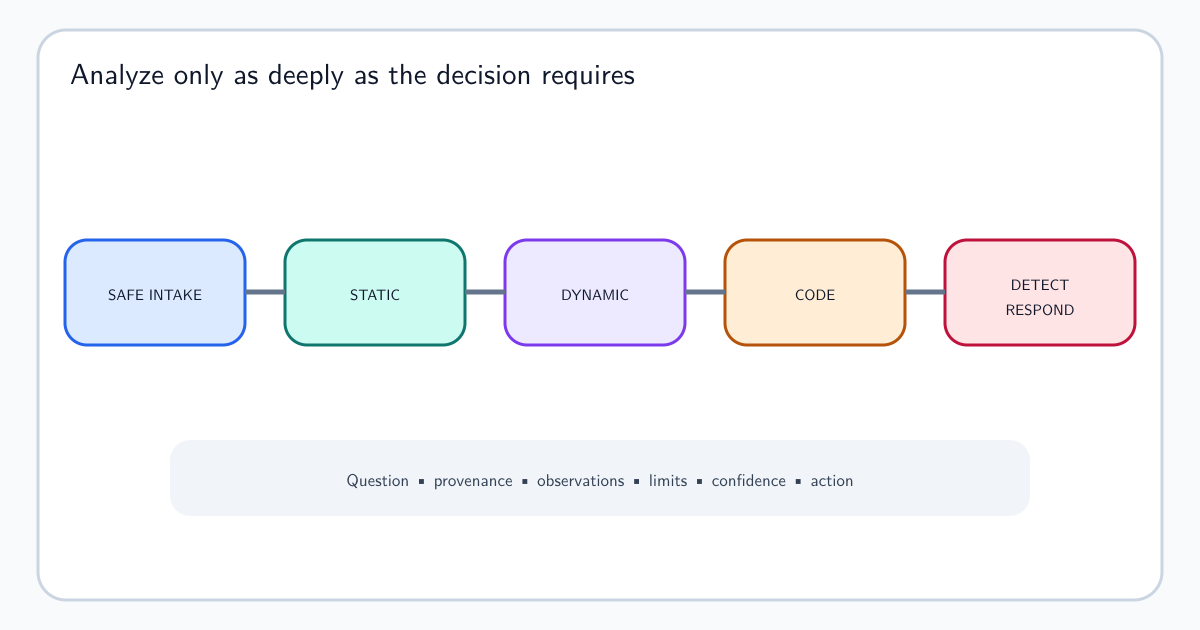
Learn how malware analysis works, from safe intake and static triage to dynamic behavior, code analysis, evidence reporting, detection, and response.
Take calm, prioritized action after suspicious access, malware, device loss, or data exposure while preserving trustworthy recovery options.
Coordinate isolation, evidence, identity containment, business continuity, restoration, and extortion decisions during a ransomware incident.
Preserve security evidence with enough context, integrity, and proportionality to support reliable investigation and action.
Follow an evidence-led incident response lifecycle from preparation and triage through recovery and durable improvement.