Network Security
mTLS Certificate Rotation Without Outages
mTLS certificate rotation without outages requires dependency mapping, overlapping trust, protected keys, staged rollout, expiry monitoring, and rollback.
Practical guidance for network security decisions and defensible security work.
12 resources
mTLS certificate rotation without outages requires dependency mapping, overlapping trust, protected keys, staged rollout, expiry monitoring, and rollback.
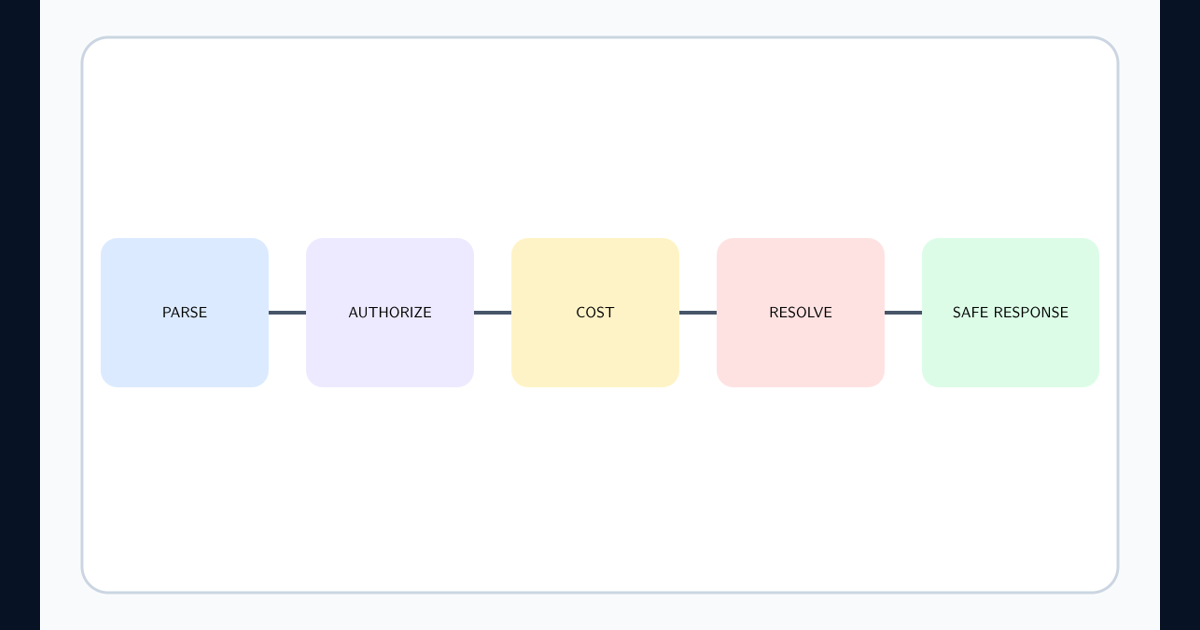
GraphQL authorization and query security combines field-level policy, object checks, depth and cost budgets, batching limits, safe errors, and telemetry.
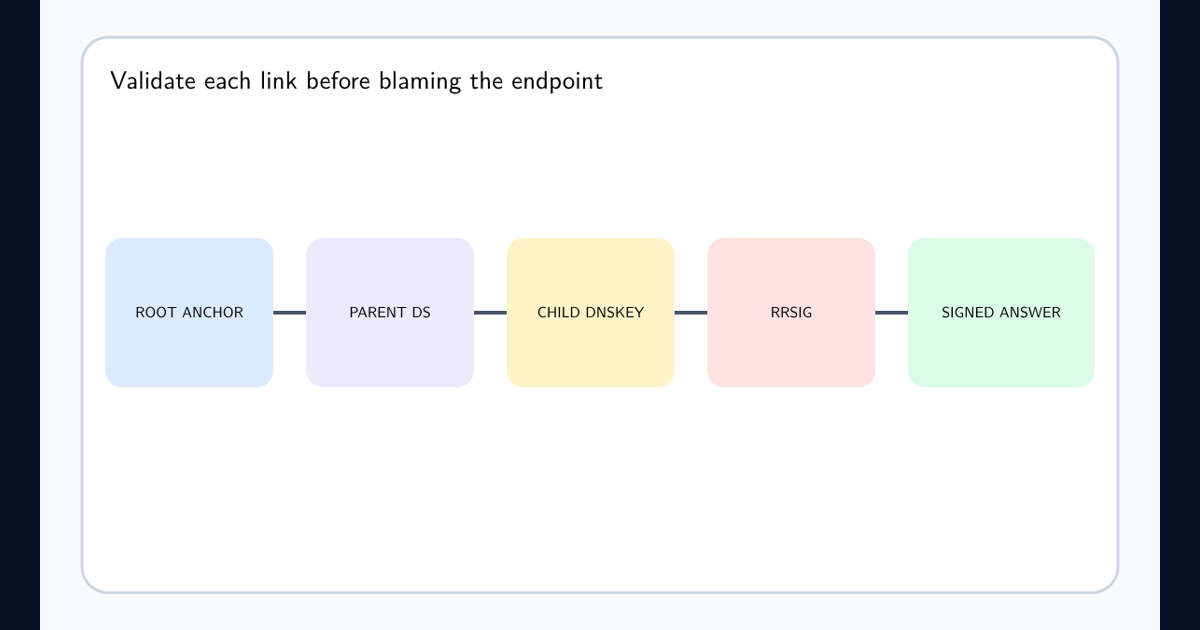
DNSSEC validation failure troubleshooting traces resolver state, delegation, DNSKEY and DS records, signatures, time, algorithms, caching, and safe recovery.
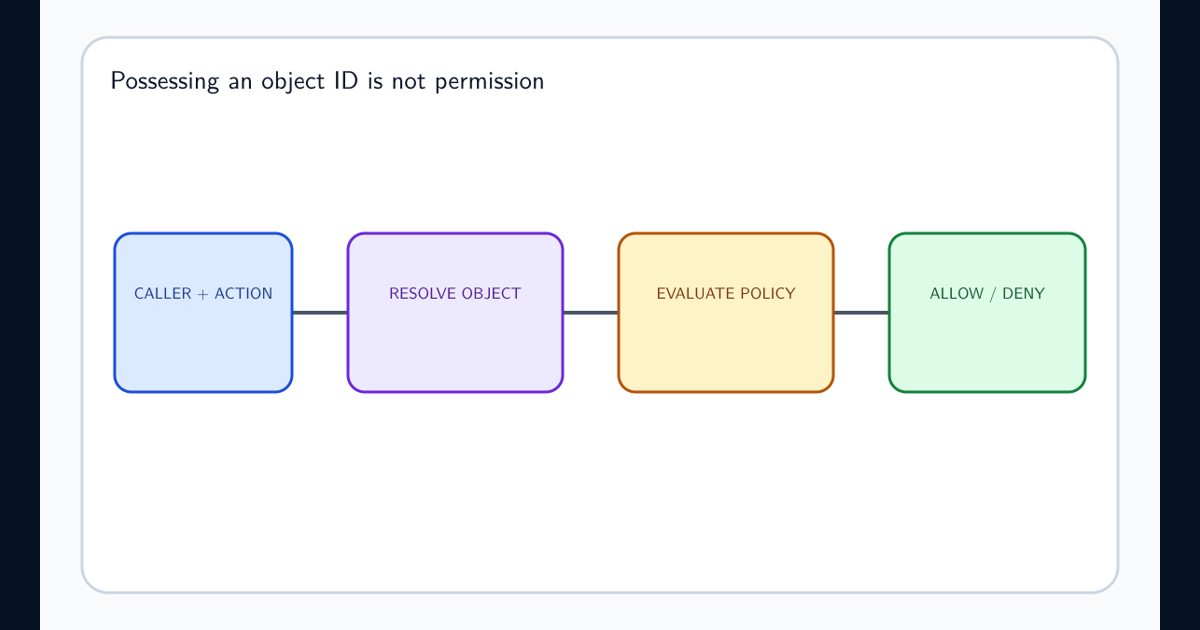
API BOLA authorization testing verifies that every object read, update, and deletion enforces the caller, action, tenant, relationship, and resource policy.
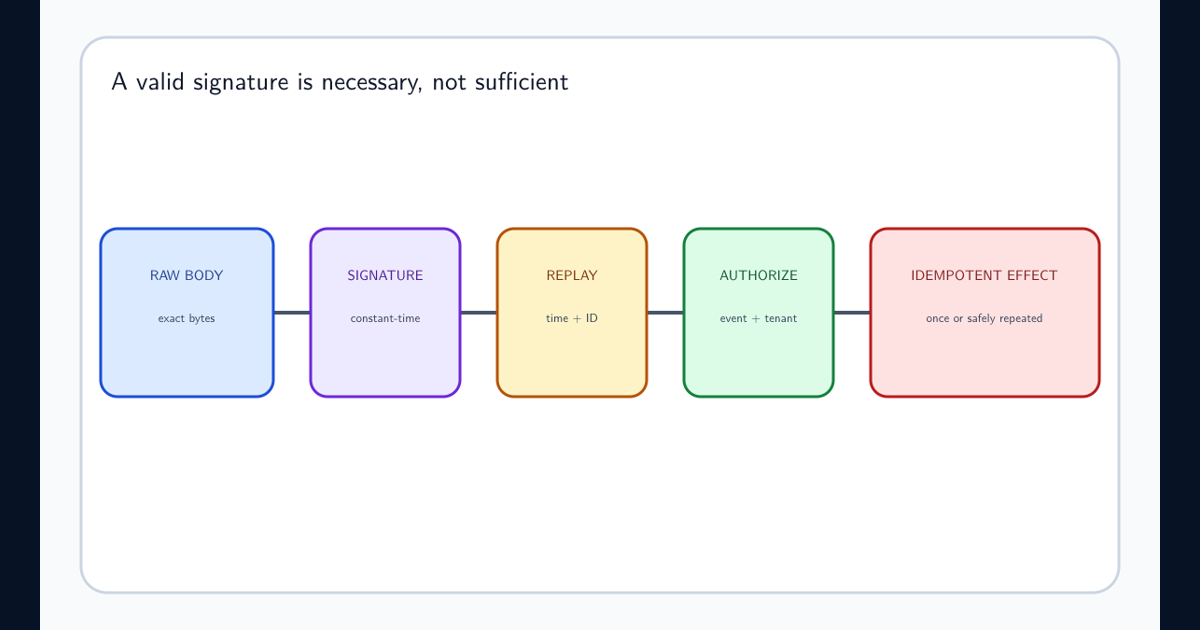
Webhook signature verification and replay defense requires raw-body validation, secret rotation, timestamp checks, delivery deduplication, and idempotency.
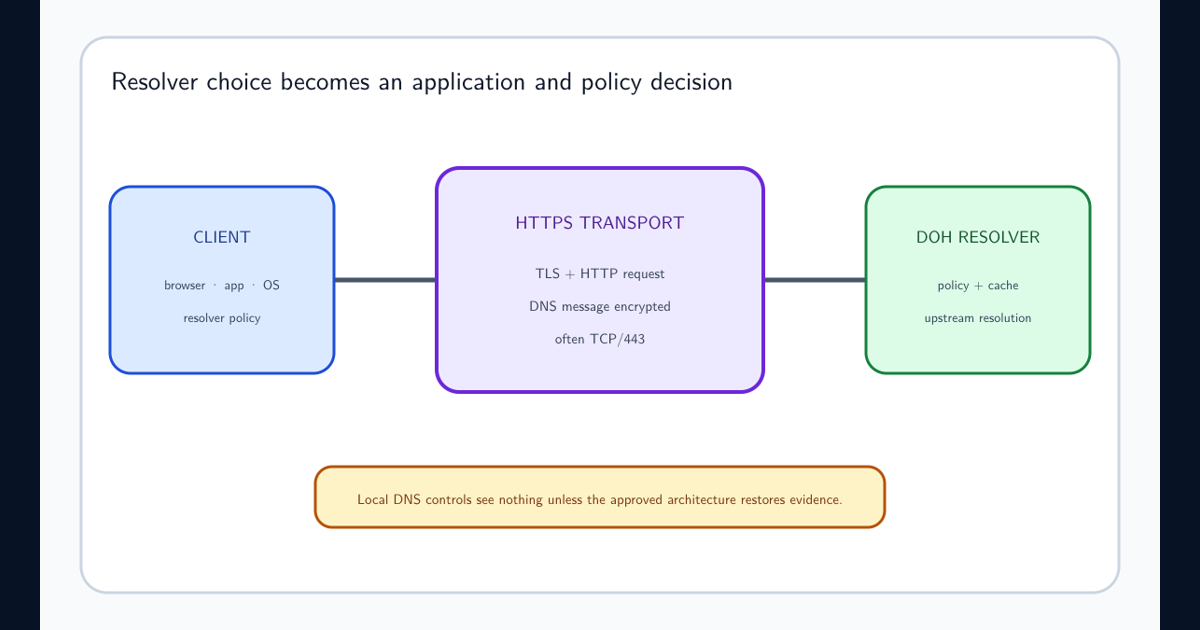
DNS over HTTPS enterprise visibility requires approved resolvers, client policy, endpoint attribution, encrypted-flow evidence, and split-DNS testing.
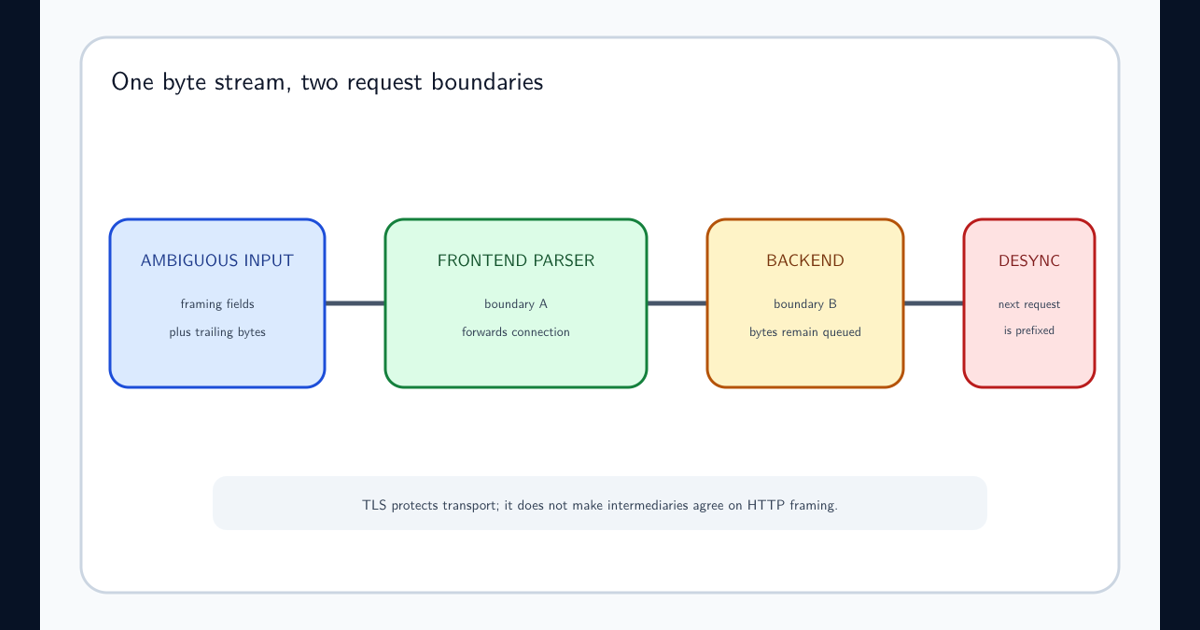
HTTP request smuggling detection finds parser disagreement, ambiguous message framing, connection desynchronization, and backend request anomalies.
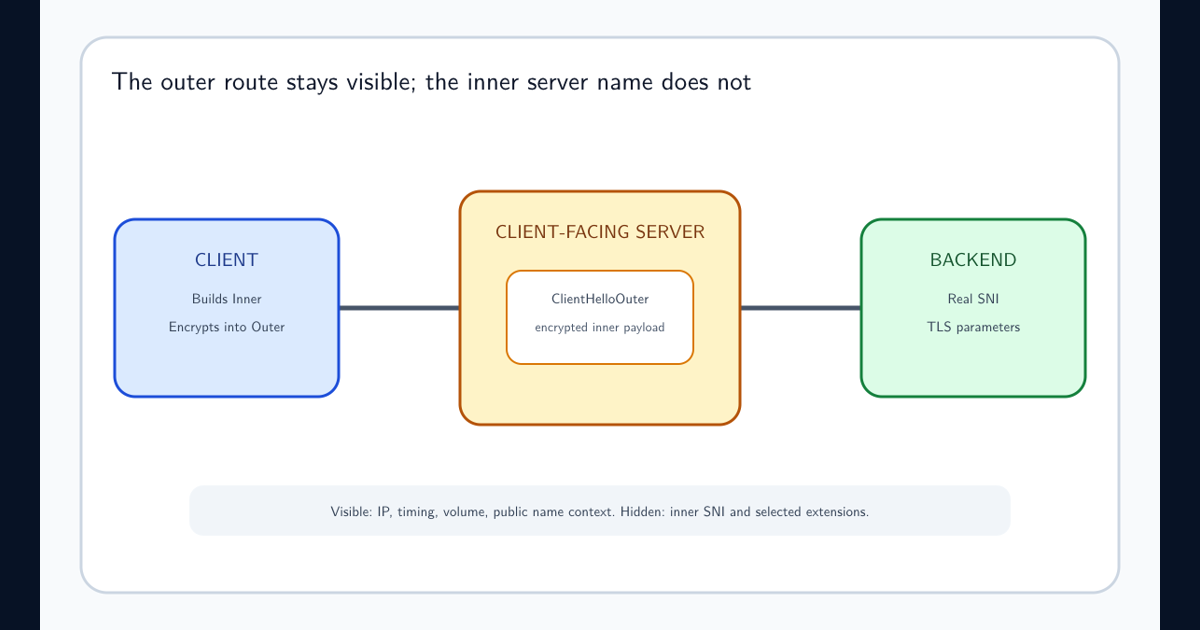
Understand Encrypted Client Hello, what ECH hides, what network evidence remains, and how defenders can redesign monitoring without blocking privacy.
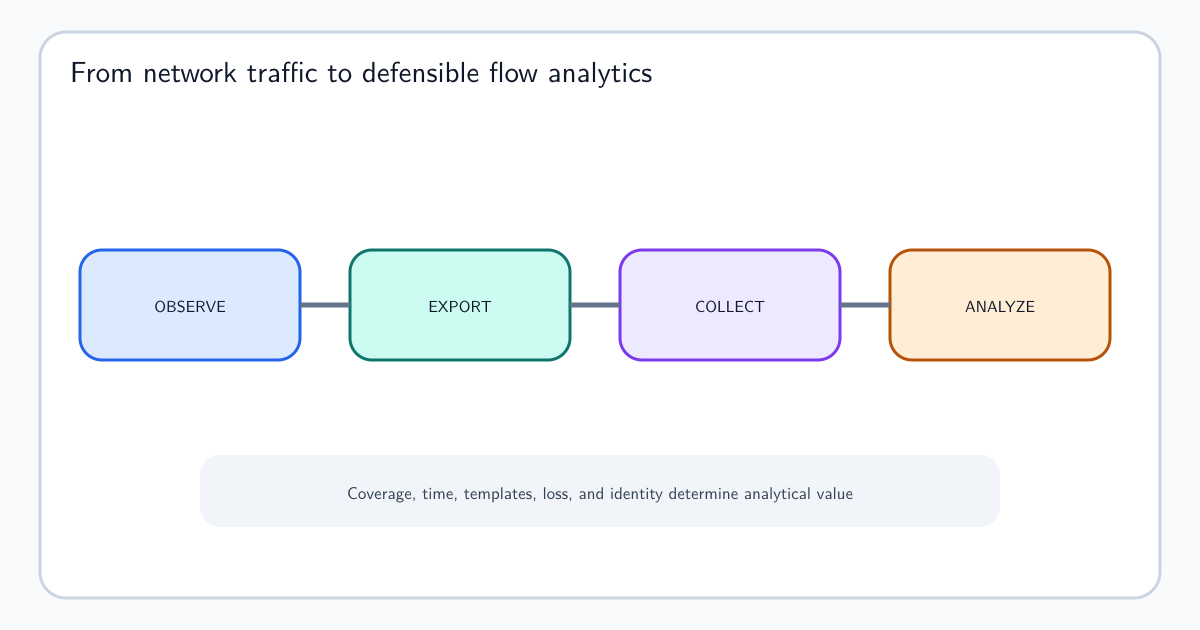
Learn how NetFlow monitoring works, which records to collect, how exporters and collectors fit together, and how security teams analyze flow data.
Use modern connection security, trustworthy destinations, careful downloads, and bounded app permissions without relying on security myths.