From Threat Model to Detection Hypothesis
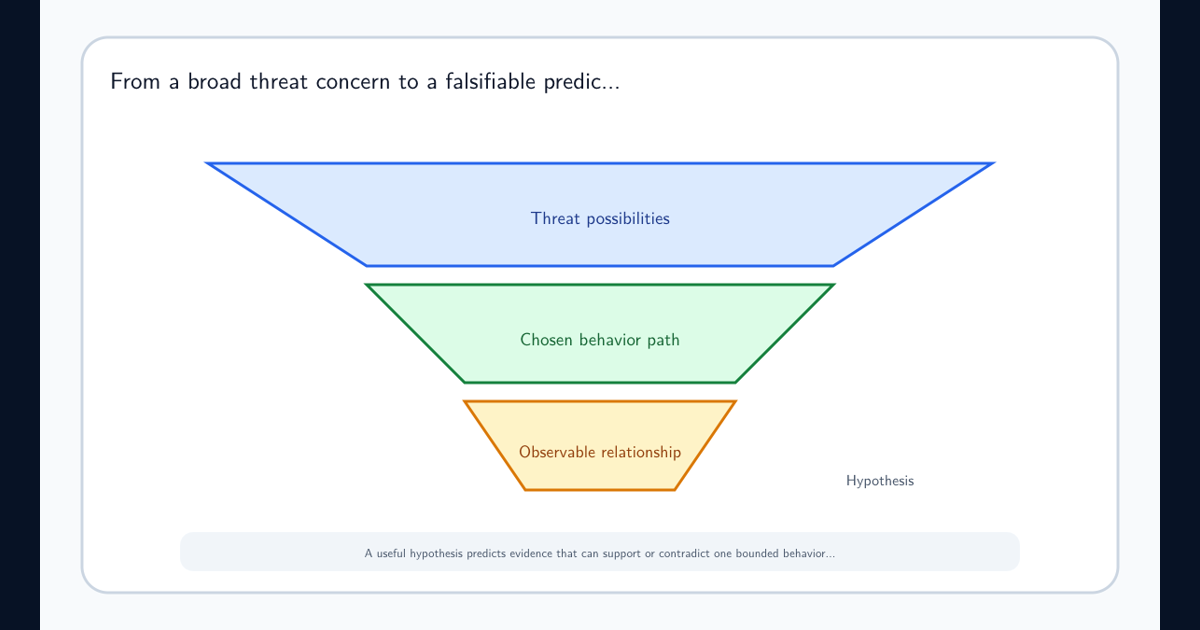
Move from a broad threat model to a falsifiable prediction about the evidence a particular behavior path should leave—and the ordinary explanations that could resemble it.
Practical guidance for detection engineering decisions and defensible security work.
67 resources
Move from a broad threat model to a falsifiable prediction about the evidence a particular behavior path should leave—and the ordinary explanations that could resemble it.
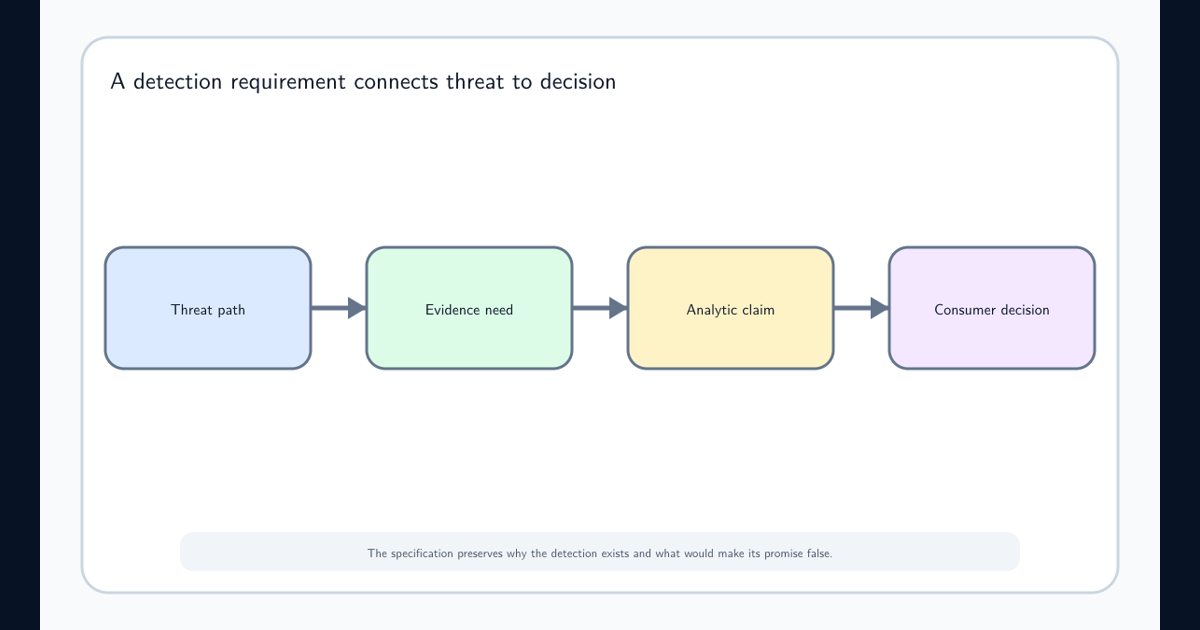
A detection requirement is the reasoning that connects a threat concern to a consumer, observable evidence, a testable claim, and an honest boundary of coverage.
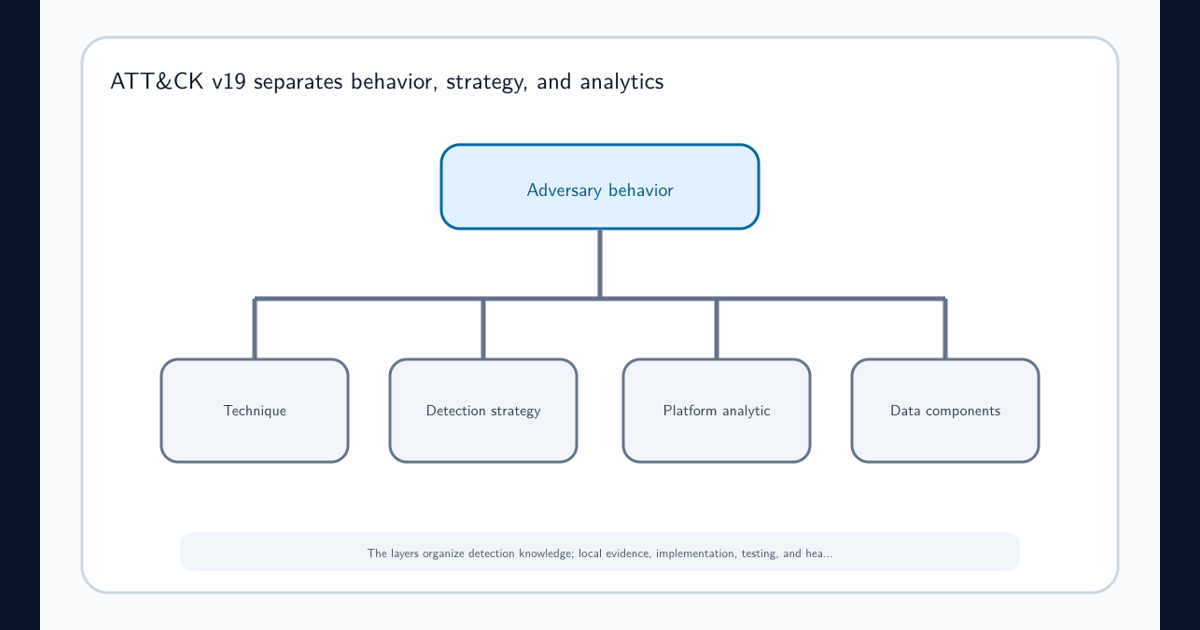
Read MITRE ATT&CK v19 detection strategies, analytics, and data components as a layered knowledge model without mistaking framework mappings for deployed coverage.
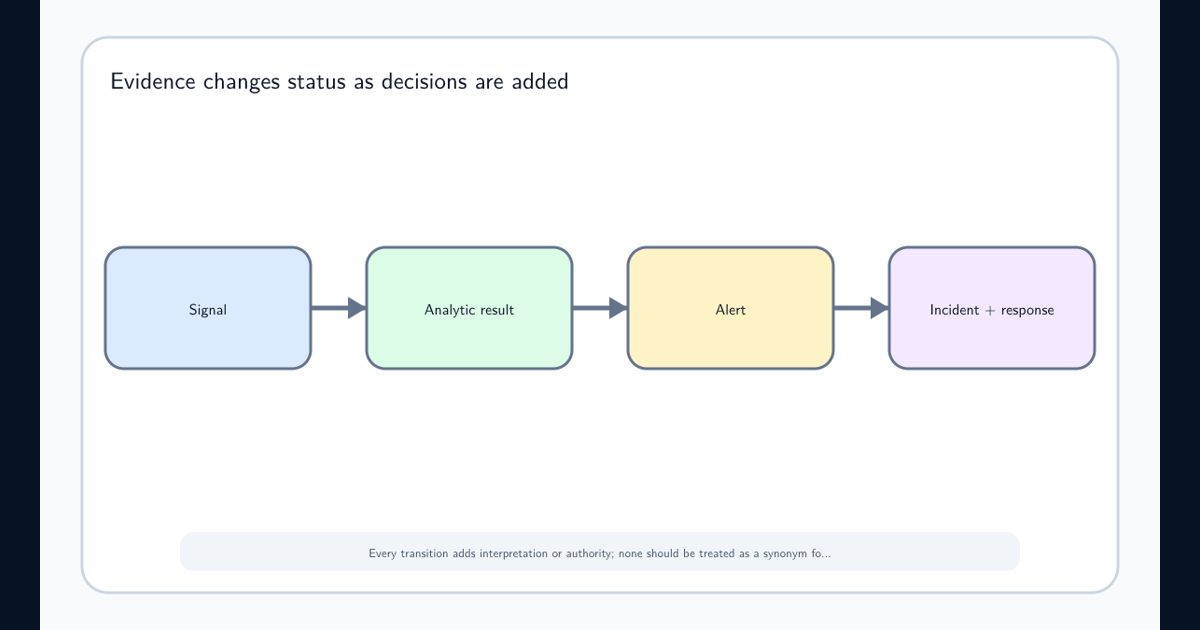
Keep signal, analytic, alert, incident, and response distinct so evidence can move through the detection service without conclusions becoming stronger by accident.
Test telemetry, logic, enrichment, alert delivery, and analyst outcomes with safe, repeatable malicious and benign scenarios.
Design, test, deploy, tune, and maintain detections as evidence-producing security controls.
Evaluate whether security telemetry has the coverage, context, timing, and stability needed for investigation and detection.