CTI Technology & Platforms
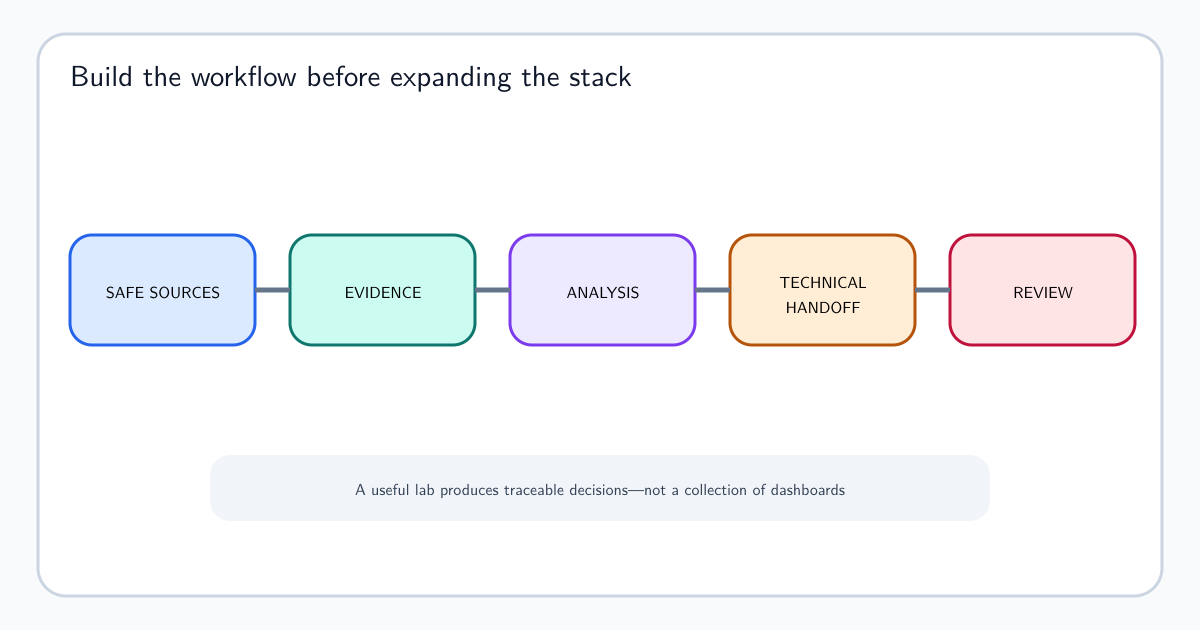
Build a Threat Intelligence Home Lab: Safe Stack and Labs
Build a safe threat intelligence home lab with isolated tooling, structured data, repeatable analysis exercises, and portfolio-ready outputs.
Practical guidance for selecting, integrating, and governing technology used in Cyber Threat Intelligence.
8 resources
Build a safe threat intelligence home lab with isolated tooling, structured data, repeatable analysis exercises, and portfolio-ready outputs.
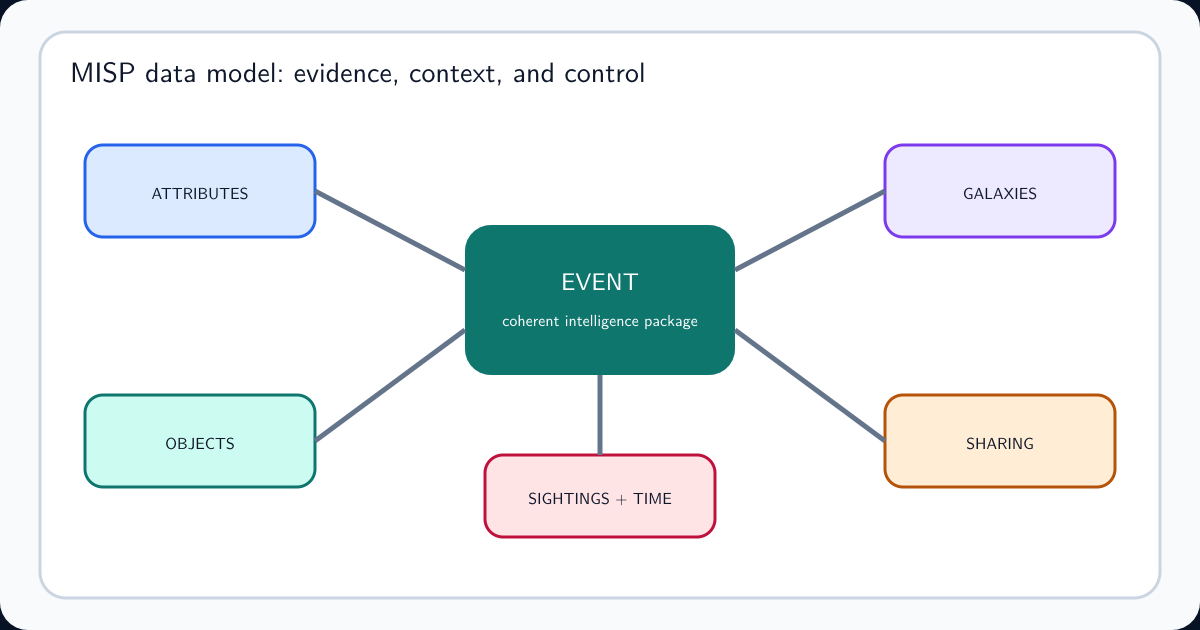
Learn the MISP data model for indicators, events, objects, threat actors, campaigns, sightings, sharing controls, correlation, and lifecycle decisions.
Decide where AI can assist CTI, protect sensitive evidence, verify every consequential claim, and retain human ownership of analytic judgments.
Design ingestion, normalization, enrichment, curation, publication, expiry, and feedback around traceable evidence and defined intelligence uses.
Decide whether relationship-heavy CTI questions justify a graph, then design entities, evidence-backed edges, time, identity, and analyst workflows.
Design intelligence flows around specific decisions, preserve context and expiry, and stop one unreliable artifact from causing action everywhere.
Choose CTI automation by repeatability, evidence quality, reversibility, and consequence while preserving judgment, accountability, and review.
Learn what a cyber threat intelligence platform does, when a TIP adds value, which capabilities matter, and how to test, select, and implement one.