How to Troubleshoot a Slow Microsoft Purview Portal and Redirect Loops
Diagnose Microsoft Purview portal slowness, navigation lag, and redirects by separating service incidents, browser state, permissions, cross-portal routing, heavy queries, and backend enforcement.
Measure the Lag Instead of Calling the Entire Portal Slow
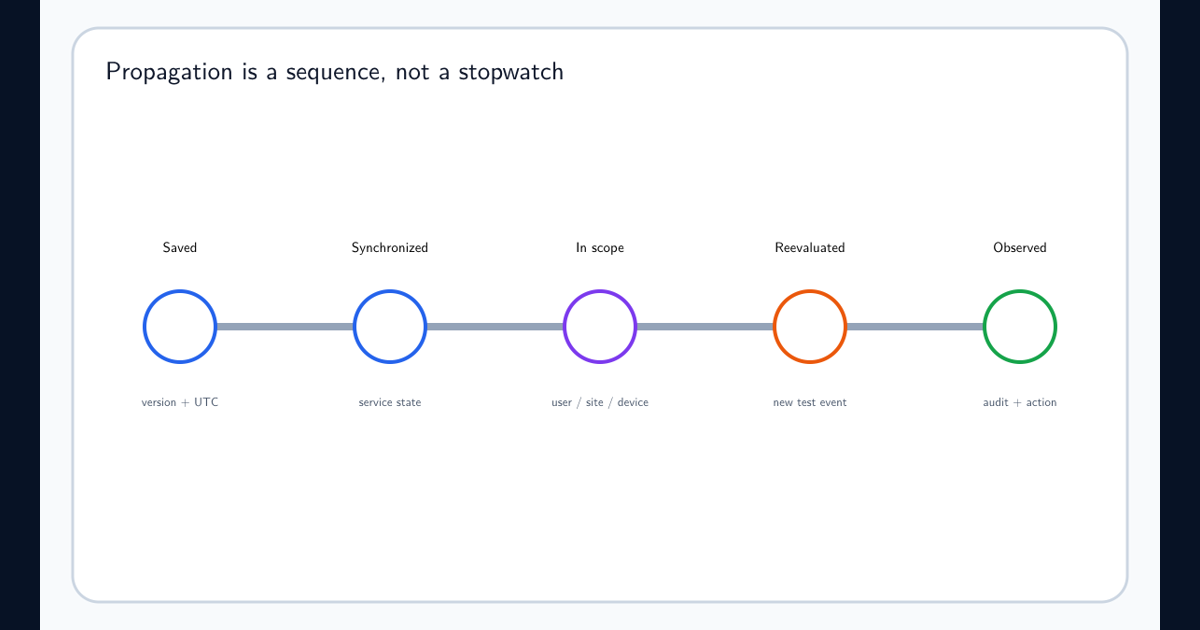
Record the exact starting URL, solution, page, action, tenant, user role, browser version, UTC time, expected result, and elapsed time. Distinguish slow initial load, blank panels, delayed table paging, save operations, search execution, repeated authentication, and redirects.
Test a lightweight page and the problem page in the same session. If only a large eDiscovery search or relationship-rich asset view is slow, workload size may be the driver. If every page stalls, browser, network, identity, or service health becomes more likely.
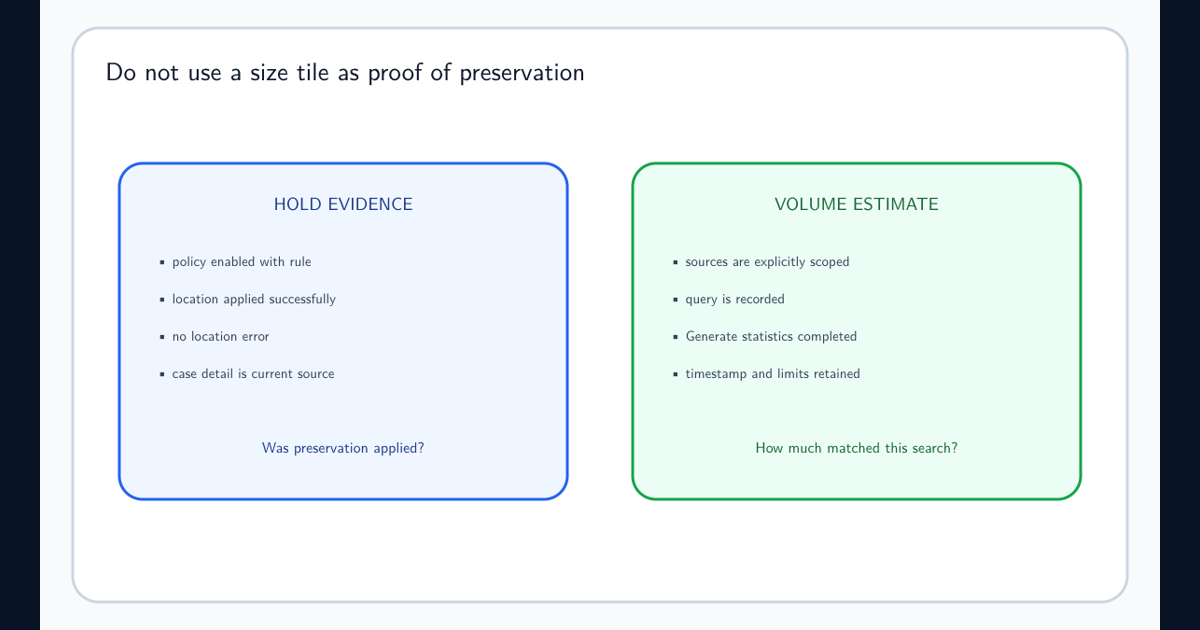
Do not use portal responsiveness as the only policy-health signal. Check distribution status, audit events, scanner results, or location details through the supported workload evidence.
Check Service Health and Published Known Issues First
Review Microsoft 365 service health for advisories or incidents affecting relevant services. If no event appears, use Report an issue when available and preserve the diagnostic time window.
Check Microsoft Purview governance known issues for documented browser and cross-portal behavior. Microsoft currently notes that some asset details from merged accounts can render in the classic governance portal while default-account assets use the new portal.
A known issue can explain the route without proving every observed delay has the same cause. Match the documented scope, status, and date to the exact symptom.
Use a Controlled Browser and Network Comparison
Reproduce once while preserving developer-tool network output or a HAR according to organizational policy. Then compare a private session, clean managed profile, another supported browser, and another approved network path. Change one variable at a time.
Check blocked scripts, third-party cookie policy, local-network restrictions, proxy inspection, conditional access, repeated token refresh, and browser extensions. Do not disable enterprise controls broadly; use an authorized diagnostic exception or known-good managed device.
Capture failing request URL, method, status, duration, redirect chain, correlation identifiers, and response size. Remove tokens and personal data before sharing traces.
Trace Redirects by Source URL, Final URL, and Feature Ownership
Old bookmarks, deep links, merged governance accounts, and features still hosted in another experience can produce legitimate cross-portal routing. Capture the full redirect chain rather than reporting only that the toggle “went back.”
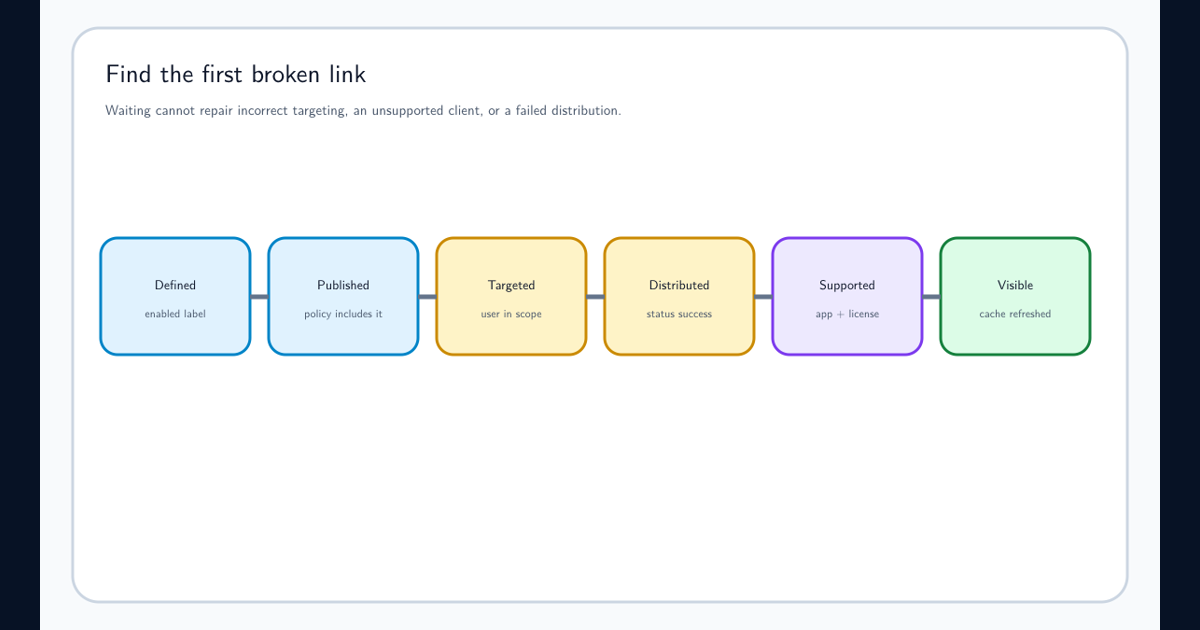
Start from purview.microsoft.com, navigate through the current solution menu, and compare the resulting route with the bookmark. Verify the user has the required role and license; authorization failures can route to generic landing pages that resemble navigation bugs.
Avoid repeatedly toggling portal preferences when the feature itself owns the destination. Use the documented current entry point and update operational runbooks.
Reduce Heavy Queries Without Confusing Performance With Correctness
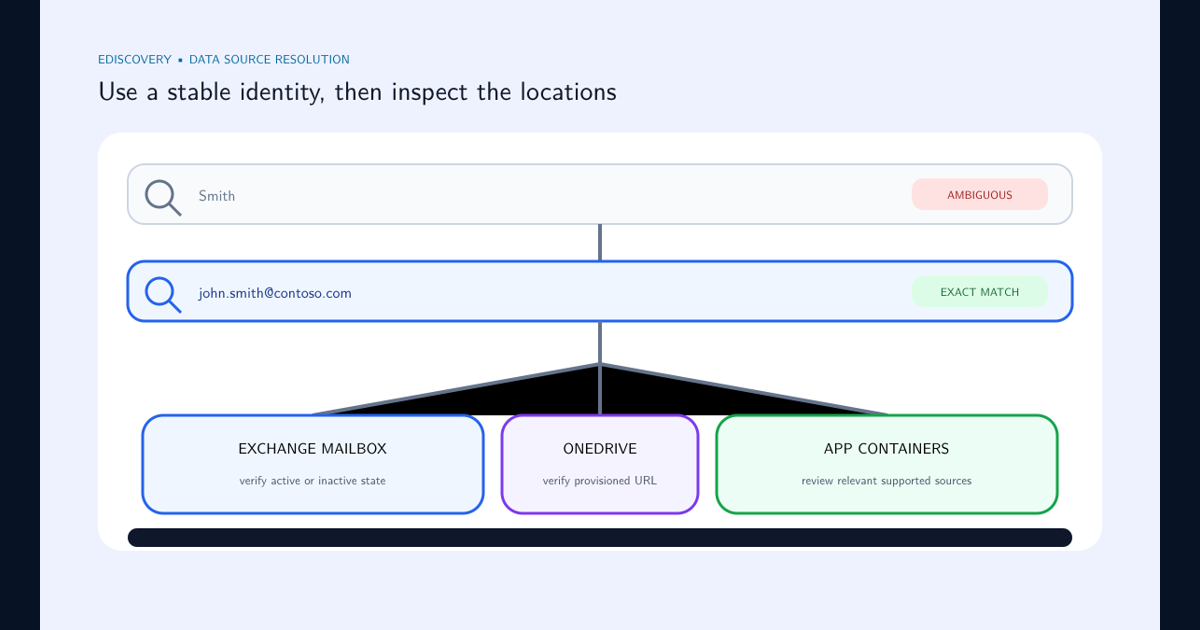
Narrow eDiscovery sources and dates, page Data Map results, avoid expanding all relationships, and filter reports before export. A slow broad query may be behaving correctly while doing excessive work.
Measure request size, result count, relationship expansion, pagination, and server timing. Keep a small control query that should return quickly. If the control is fast and the production query is slow, optimize scope rather than clearing the browser repeatedly.
Do not narrow a legal hold or investigation merely to improve speed without authorized scope review. Performance changes must preserve the business or legal requirement.
Escalate With Reproducible Portal and Backend Evidence
Run relevant Microsoft Purview self-help diagnostics for DLP, labels, holds, audit, or encryption. These validate configuration even when the interactive page is unreliable.
Provide support with tenant and workload, UTC time, source and final URLs, affected population, roles, browser build, network path, HAR or request IDs, screenshots, service-health status, control-query comparison, and backend policy evidence. Redact credentials and content.
A good escalation lets Microsoft distinguish portal rendering, API latency, permission evaluation, rollout routing, and workload processing without asking the administrator to recreate production state.
Frequently asked questions
Does a slow Purview portal mean DLP or retention stopped working?
Not necessarily. The portal is an administration surface. Verify backend policy status and workload evidence independently before concluding enforcement failed.
Why can a Purview page redirect to a classic experience?
Some features, merged governance accounts, deep links, and rollout states can route between current and classic experiences. Microsoft documents specific known cross-portal behavior; capture the source and final URL before troubleshooting.
Should browser cache always be cleared first?
Use a private session or clean browser profile as a controlled comparison. Clearing state can help isolate stale client data but also destroys evidence, so capture the reproduction and network details first.