Identity and Access Security
Windows LAPS Deployment and Security Guide
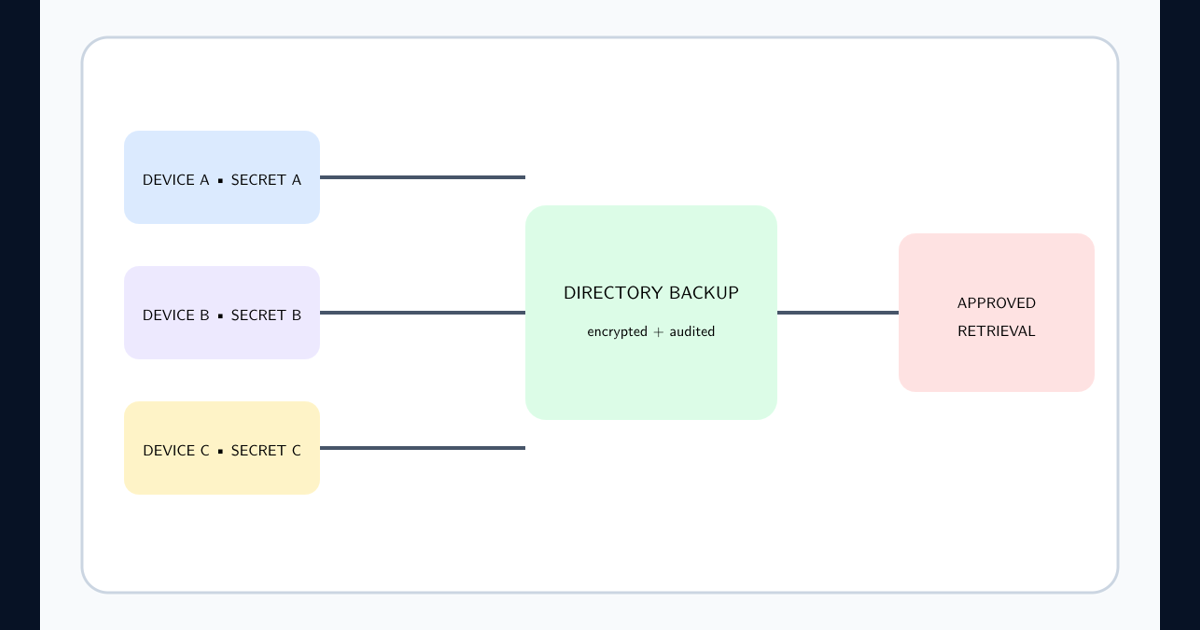
Windows LAPS deployment security covers account choice, directory preparation, encryption, retrieval rights, rotation, auditing, rollout, and recovery.
Authentication, federation, authorization, sessions, workload identity, and access governance.
7 resources
Windows LAPS deployment security covers account choice, directory preparation, encryption, retrieval rights, rotation, auditing, rollout, and recovery.
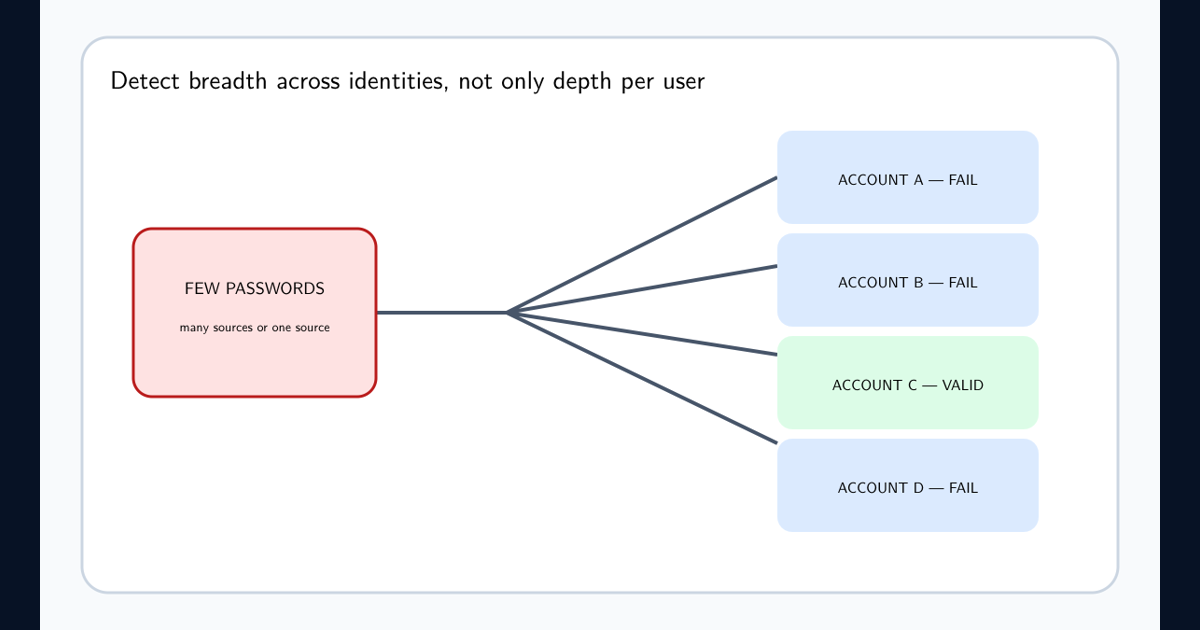
Password spraying detection correlates authentication failures across accounts, protocols, sources, time windows, MFA outcomes, and successful access.
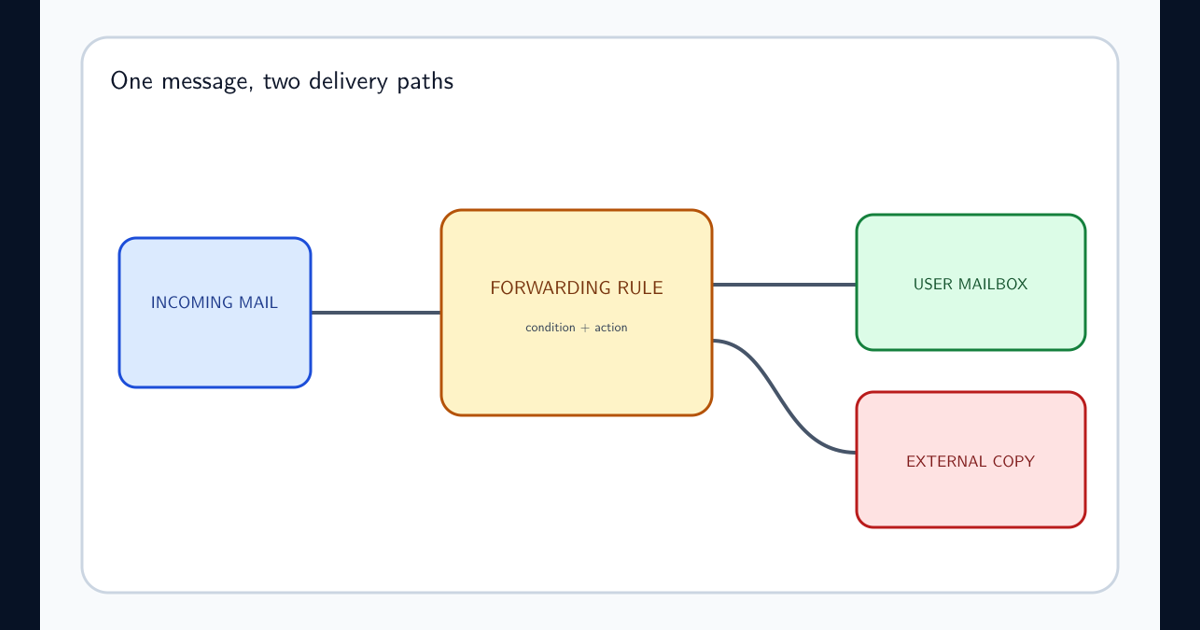
Malicious email forwarding rule detection correlates rule changes, destinations, sign-ins, message traces, mailbox access, audit evidence, and persistence.
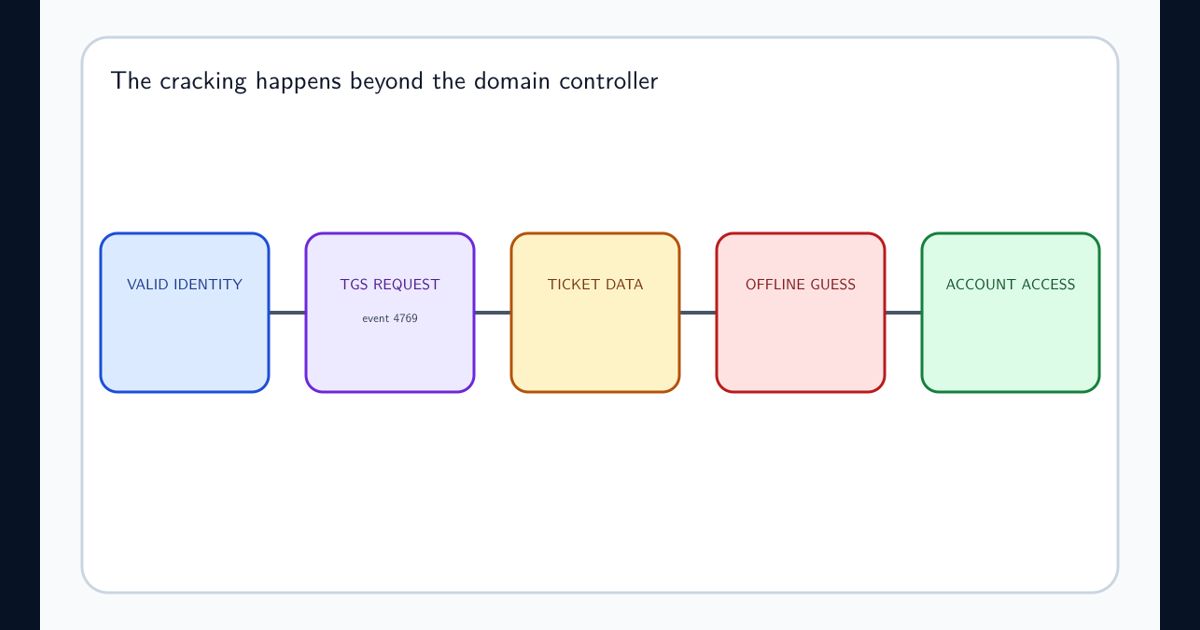
Kerberoasting detection and response uses TGS request context, encryption types, account baselines, service-account hardening, and credential recovery.
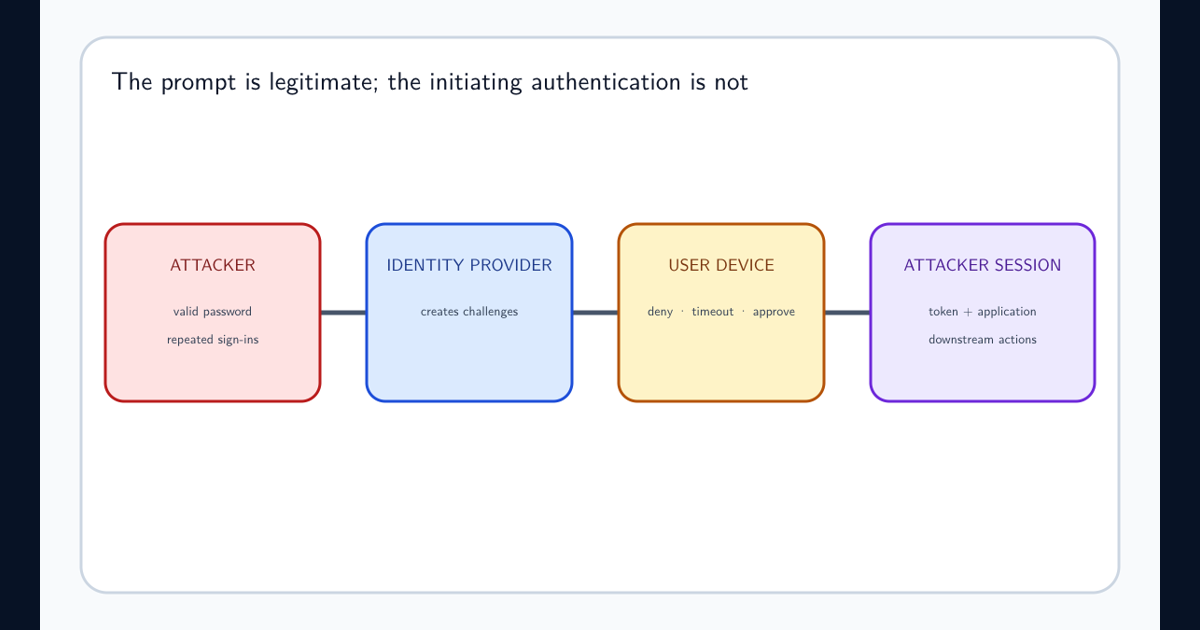
MFA fatigue attack detection correlates repeated prompts, password attempts, user denials, approval context, session creation, and downstream account use.
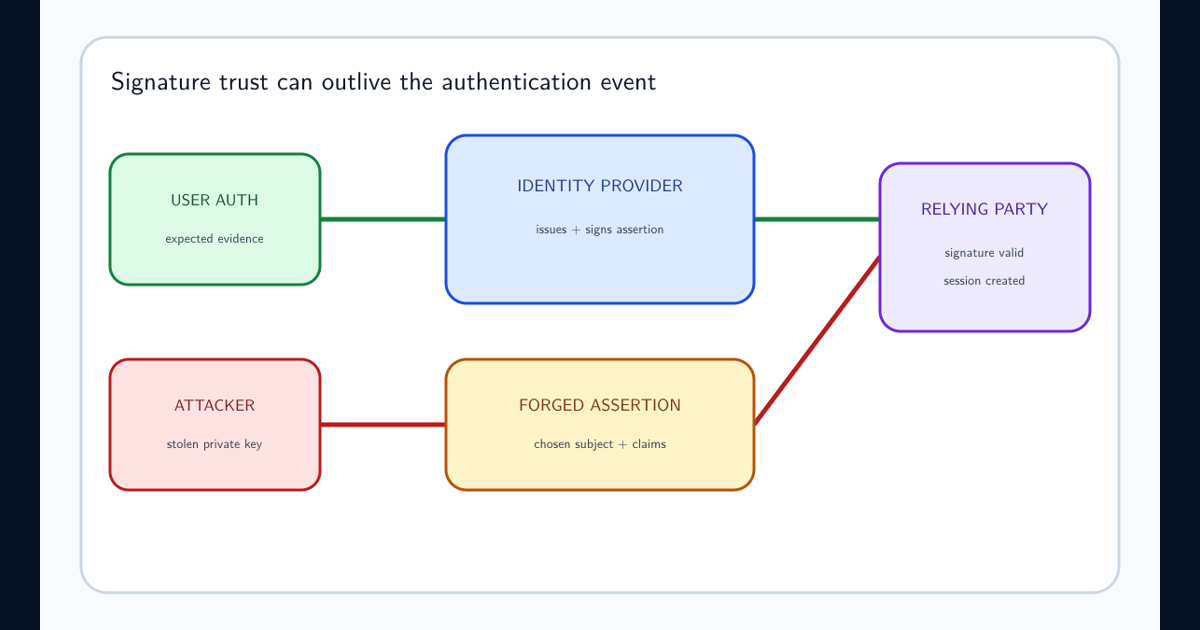
Golden SAML detection correlates federated sign-ins with assertion claims, signing keys, identity-provider issuance, MFA context, and relying-party use.
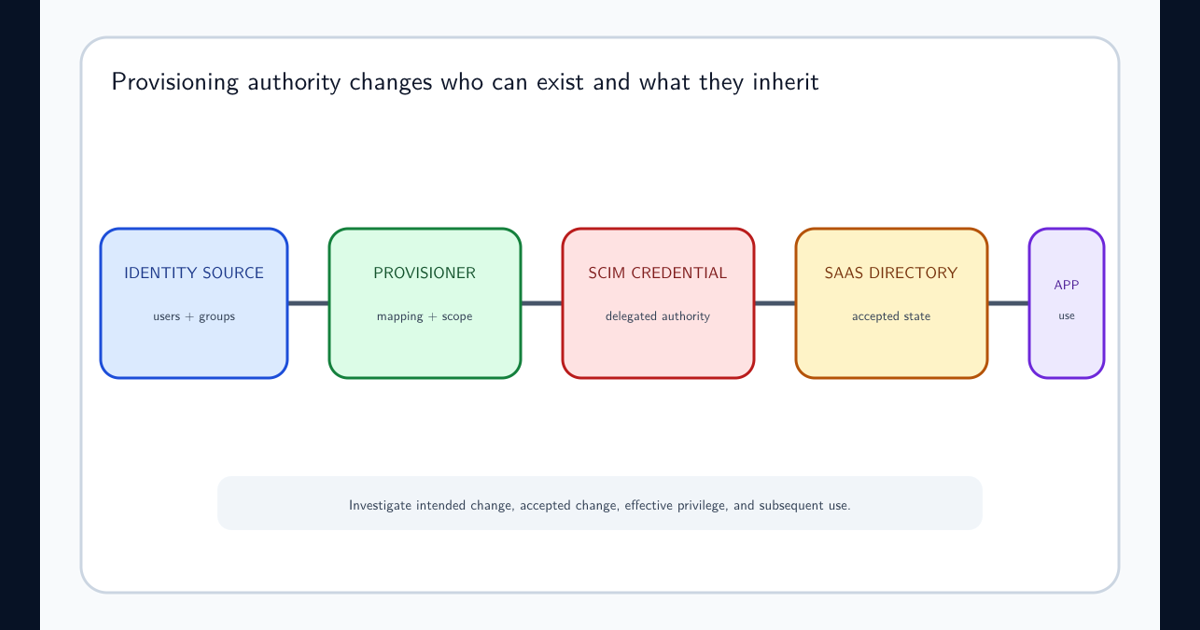
SCIM token compromise detection correlates provisioning configuration, client authentication, user and group mutations, and downstream access.