Cloud Security
Service Principal Credential Compromise Response
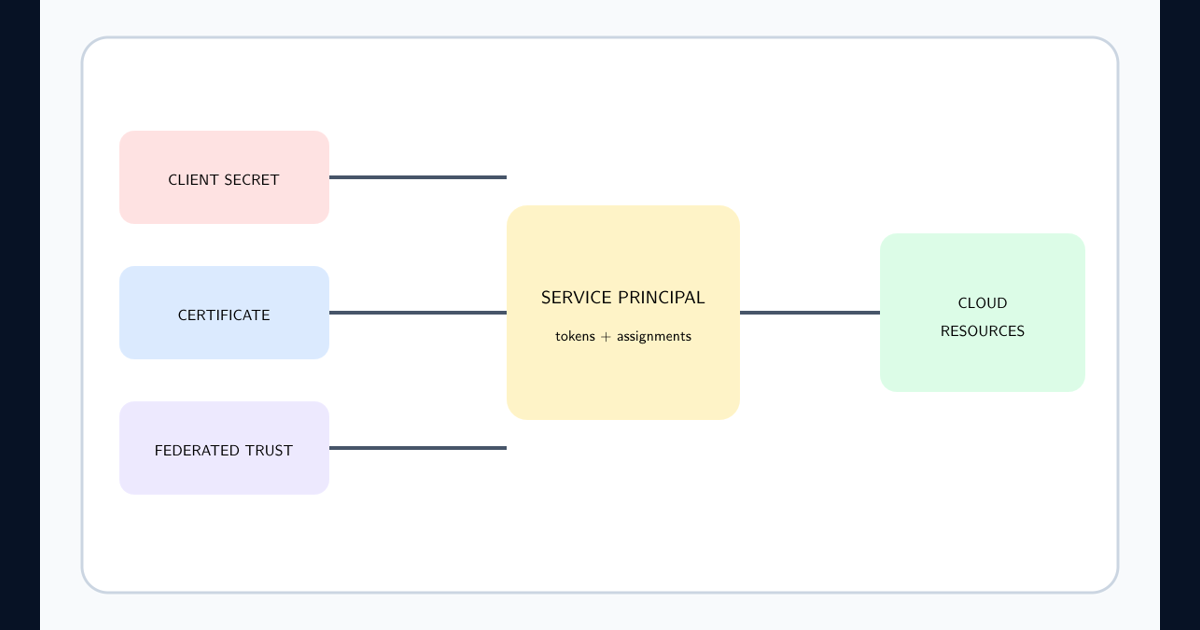
Service principal credential compromise response maps added credentials, token issuance, permissions, resource access, persistence, containment, and recovery.
Practical guidance for securing cloud identities, workloads, control planes, and shared operational responsibilities.
6 resources
Service principal credential compromise response maps added credentials, token issuance, permissions, resource access, persistence, containment, and recovery.
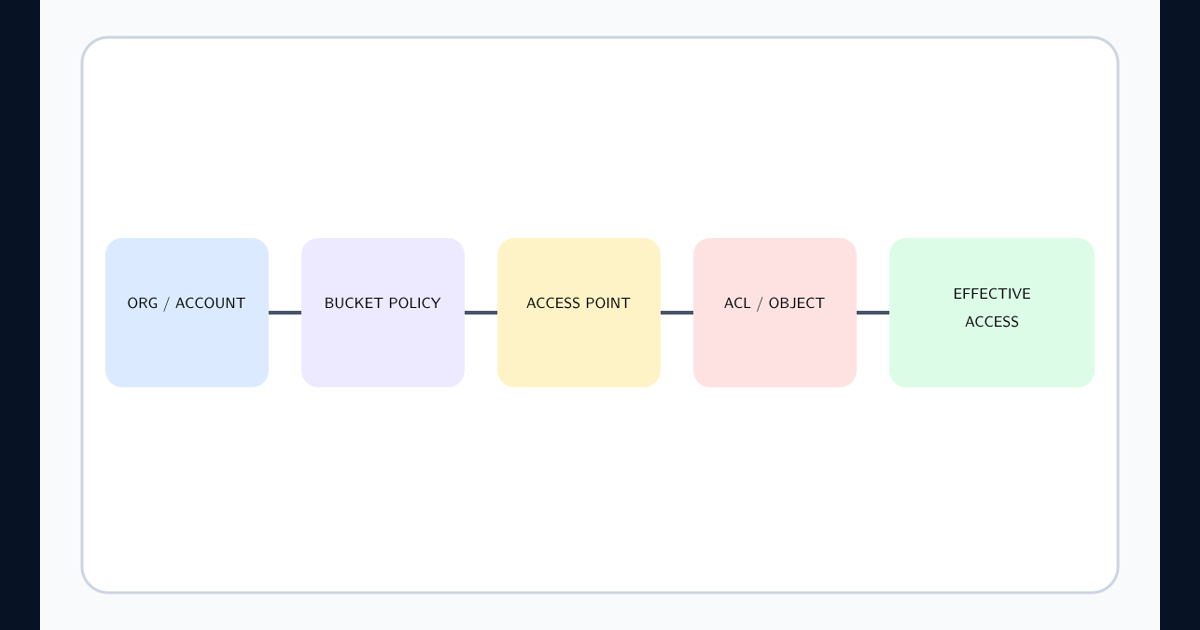
Public cloud storage exposure detection evaluates effective policies, ACLs, access points, anonymous requests, sensitive objects, change actors, and recovery.
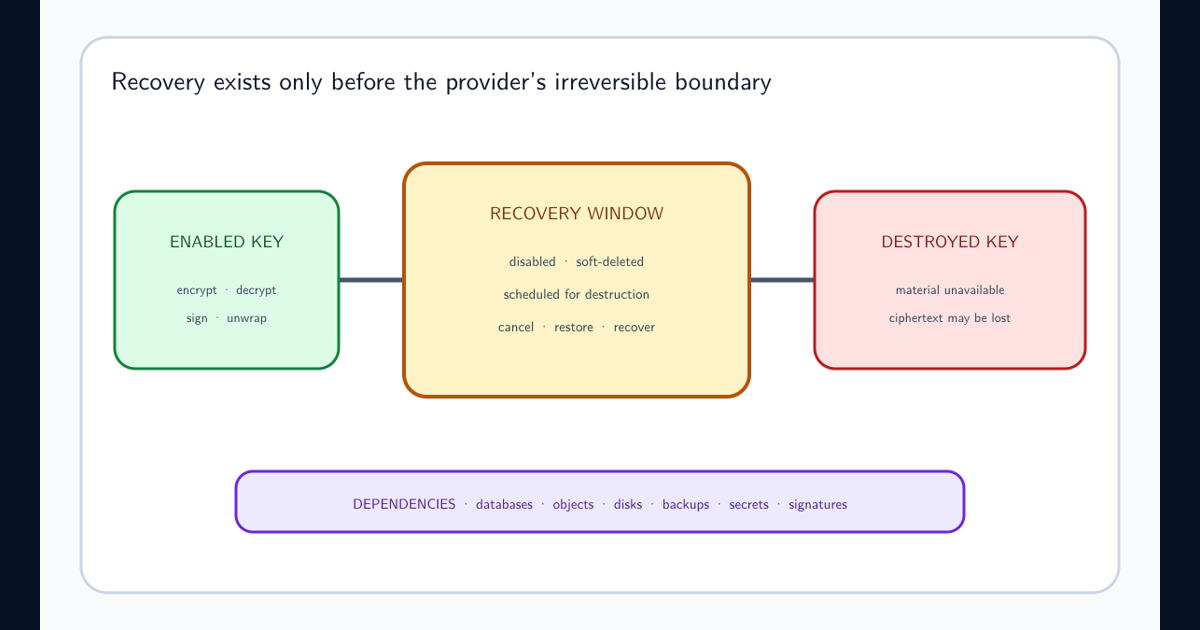
Cloud KMS key deletion detection covers destructive requests, recovery windows, dependency mapping, unusable ciphertext, purge controls, and restoration.
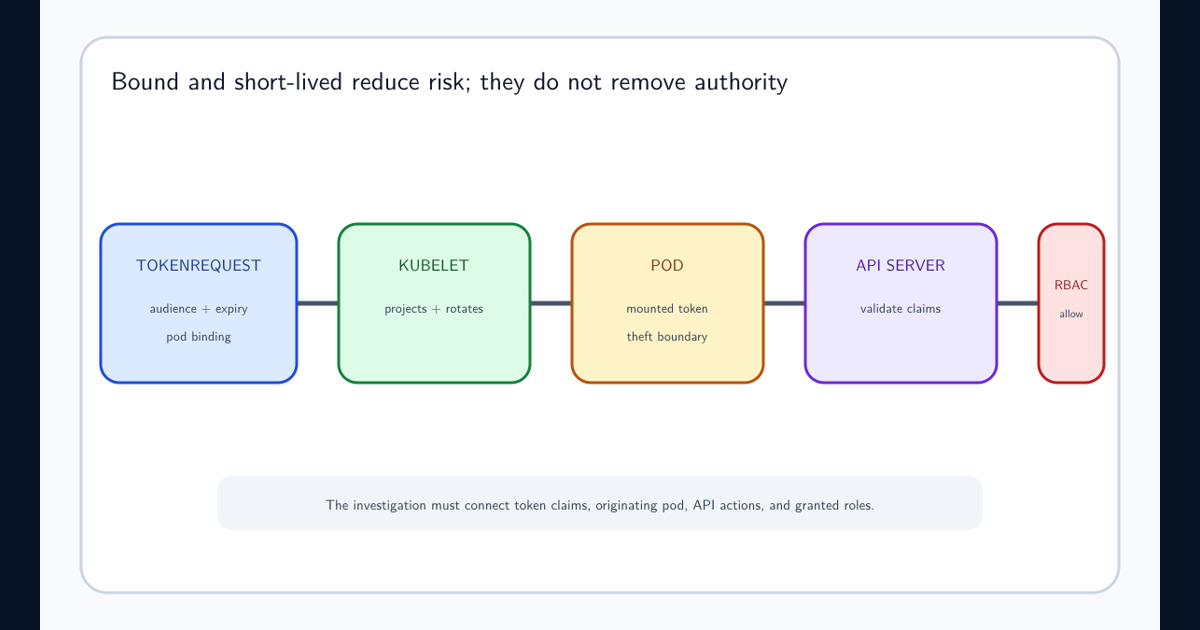
Detect Kubernetes service account token theft through token claims, pod identity, API audit events, RBAC scope, audience, and workload behavior.
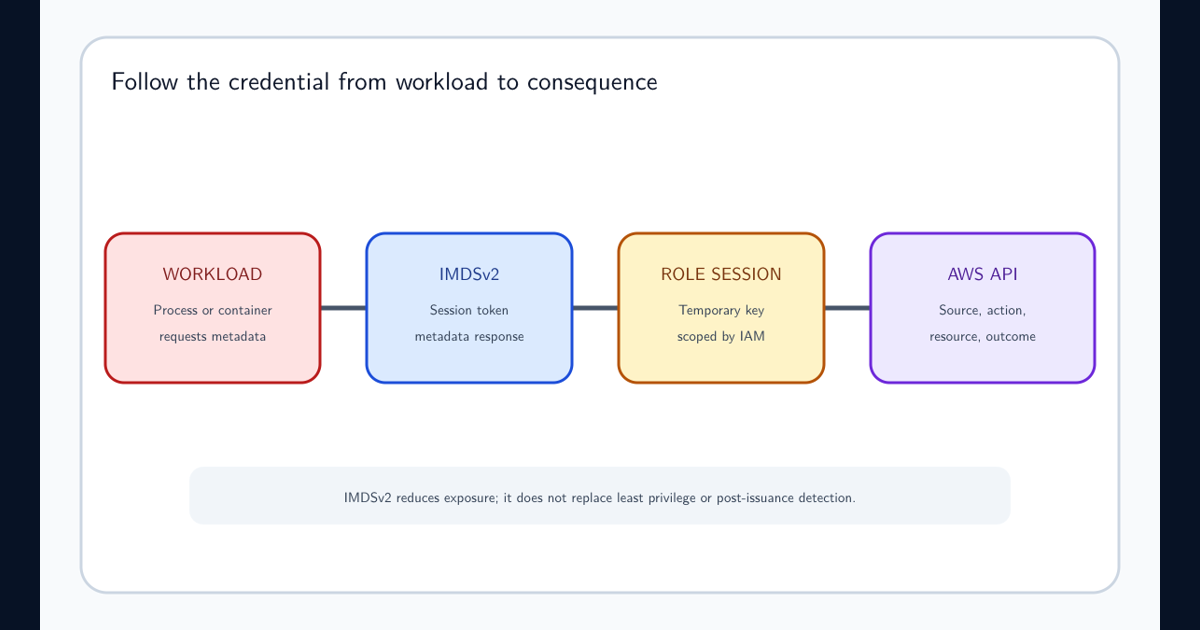
Detect AWS IMDSv2 credential theft with metadata configuration, CloudTrail evidence, GuardDuty findings, and staged EC2 hardening.
Translate cloud shared responsibility into testable ownership for identity, configuration, workloads, SaaS integrations, evidence, and recovery.