Identity & Access Security
OAuth Device Code Phishing: Detection and Response
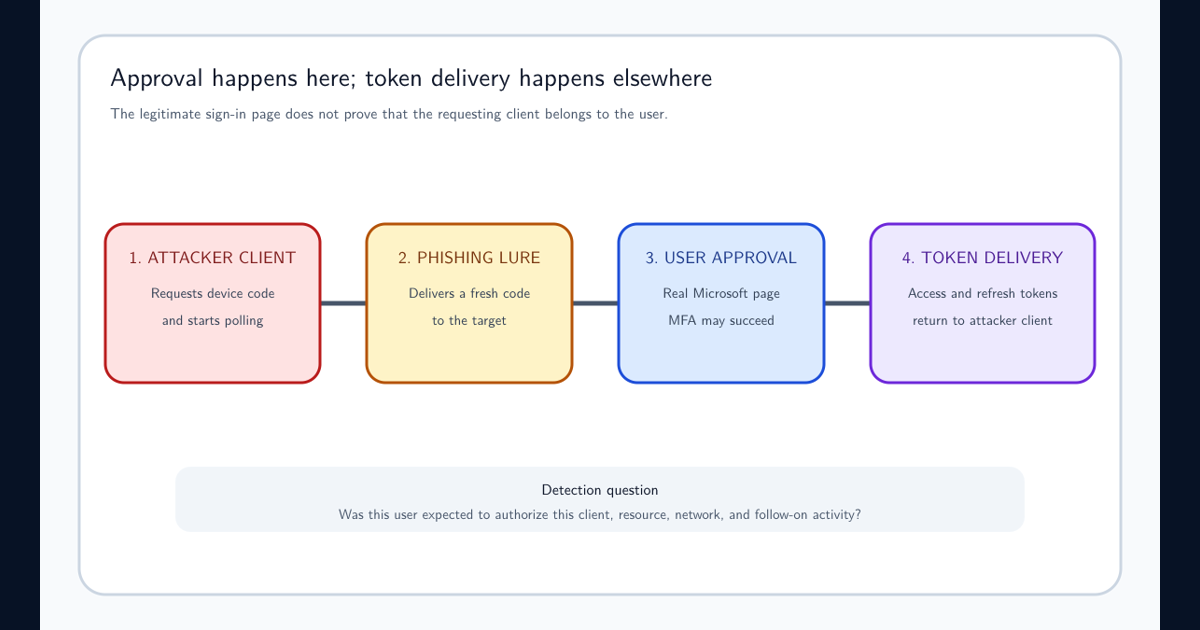
Detect OAuth device code phishing in Microsoft Entra ID using sign-in evidence, KQL correlation, containment steps, and staged Conditional Access.
Security considerations for OAuth-based delegated authorization.
3 resources
Detect OAuth device code phishing in Microsoft Entra ID using sign-in evidence, KQL correlation, containment steps, and staged Conditional Access.
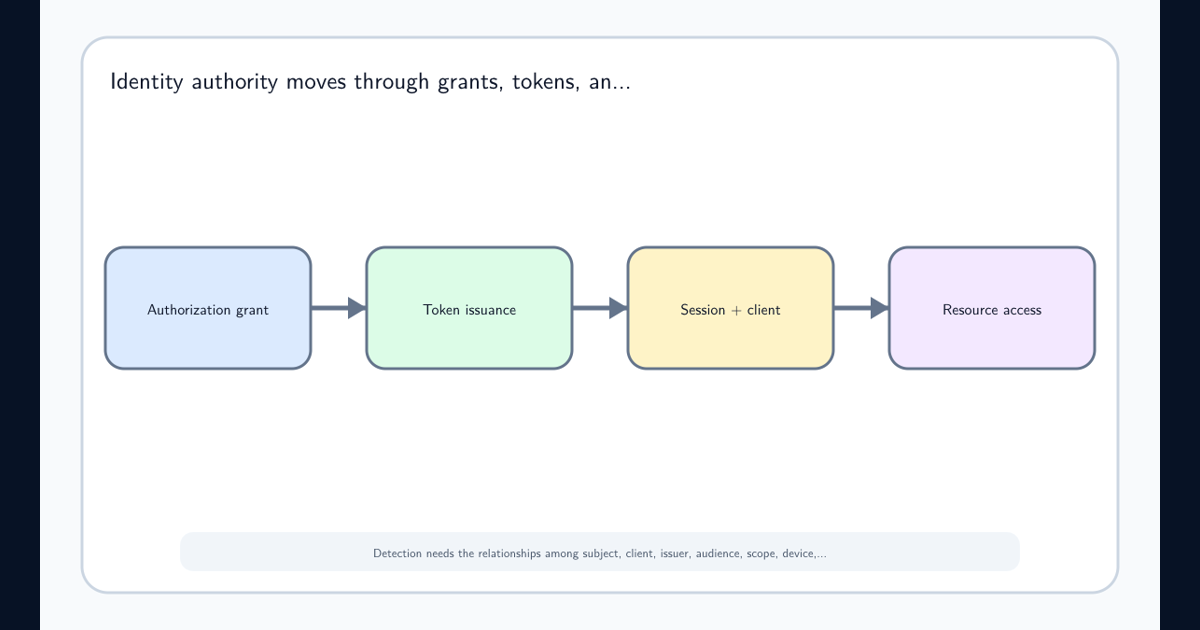
Detect identity abuse by separating grants, tokens, sessions, clients, and resource access, then reasoning about issuance, binding, rotation, revocation, and replay evidence.
Understand delegated access, consent grants, scopes, tokens, connected-app risk, and the evidence needed to investigate or revoke access safely.