Endpoint Security
Linux eBPF Abuse: Detection and Hardening
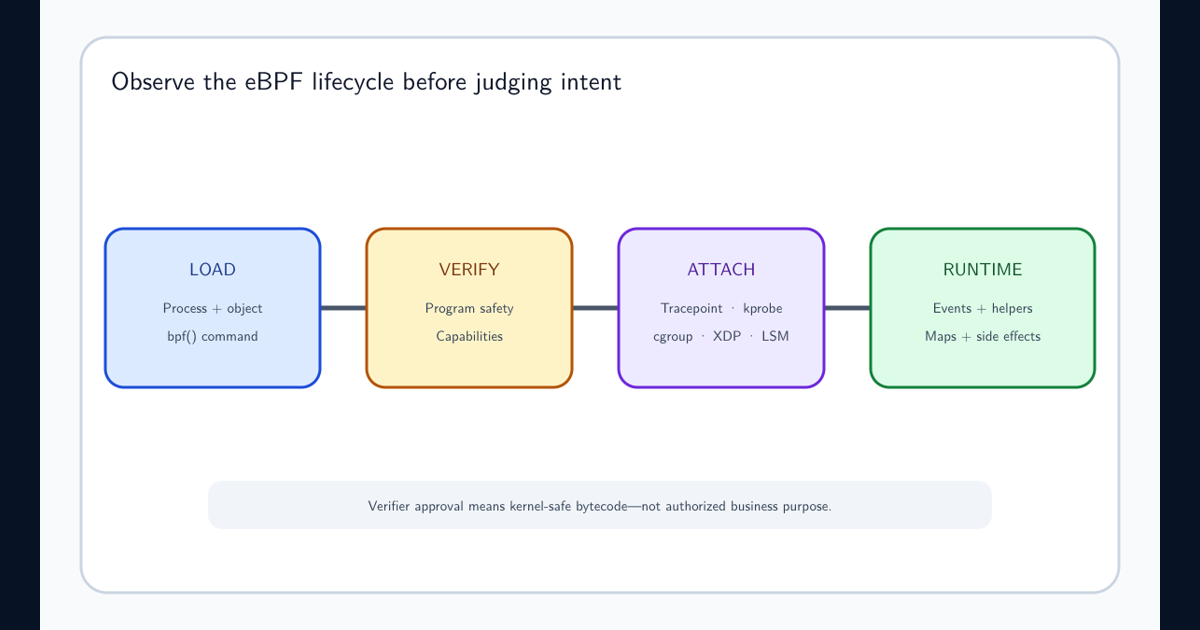
Detect Linux eBPF abuse by inventorying loaded programs, maps, links, loaders, capabilities, attachment points, and resulting endpoint behavior.
Evidence-led detection of stealth and kernel-adjacent manipulation.
1 resource
Detect Linux eBPF abuse by inventorying loaded programs, maps, links, loaders, capabilities, attachment points, and resulting endpoint behavior.