SSH Authorized Keys Persistence: Detection and Response
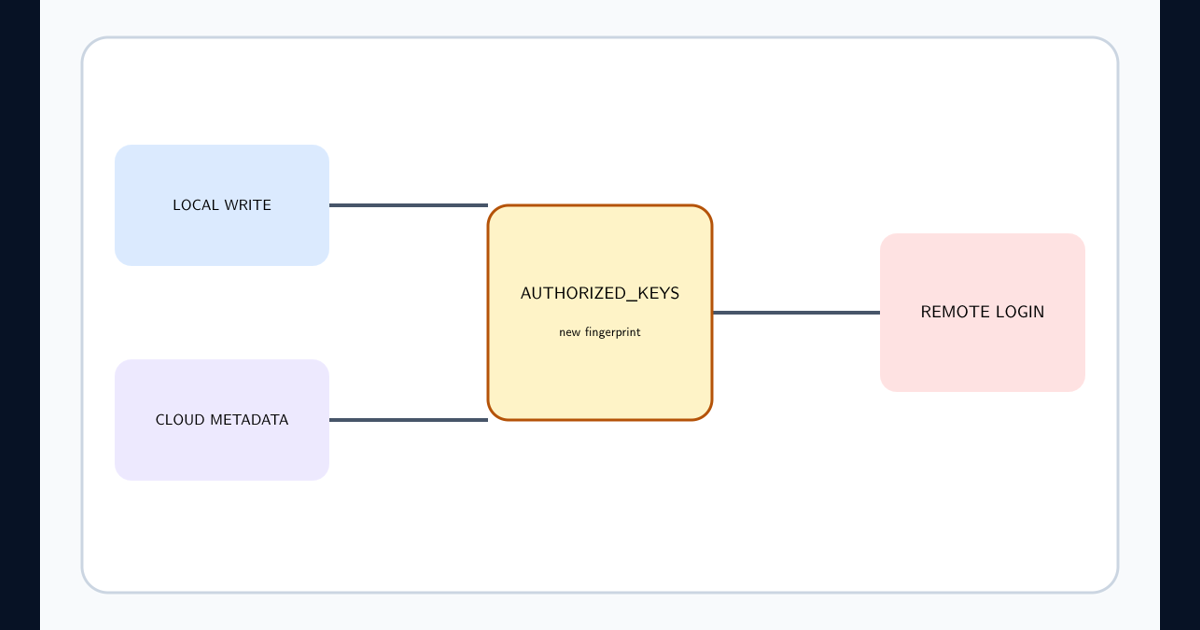
SSH authorized_keys persistence detection covers file changes, cloud metadata, key fingerprints, writers, login evidence, scope, containment, and hardening.
Practical guidance for protecting and investigating devices where people and applications work.
5 resources
SSH authorized_keys persistence detection covers file changes, cloud metadata, key fingerprints, writers, login evidence, scope, containment, and hardening.
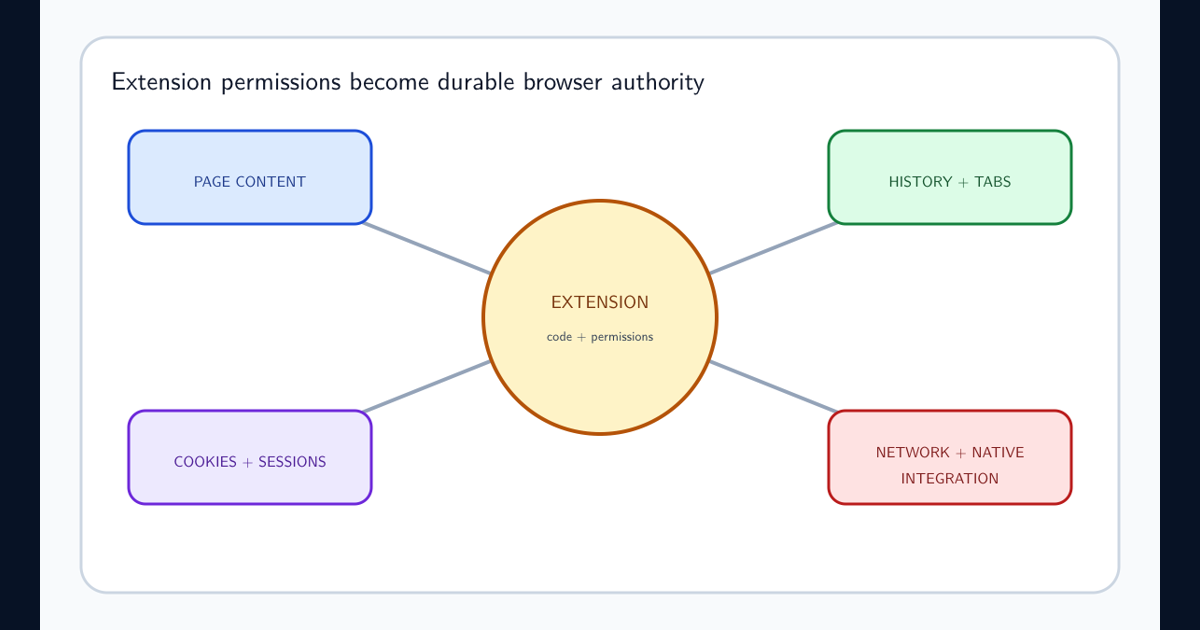
Malicious browser extension detection combines extension identity, permissions, install source, update provenance, runtime behavior, and browser policy.
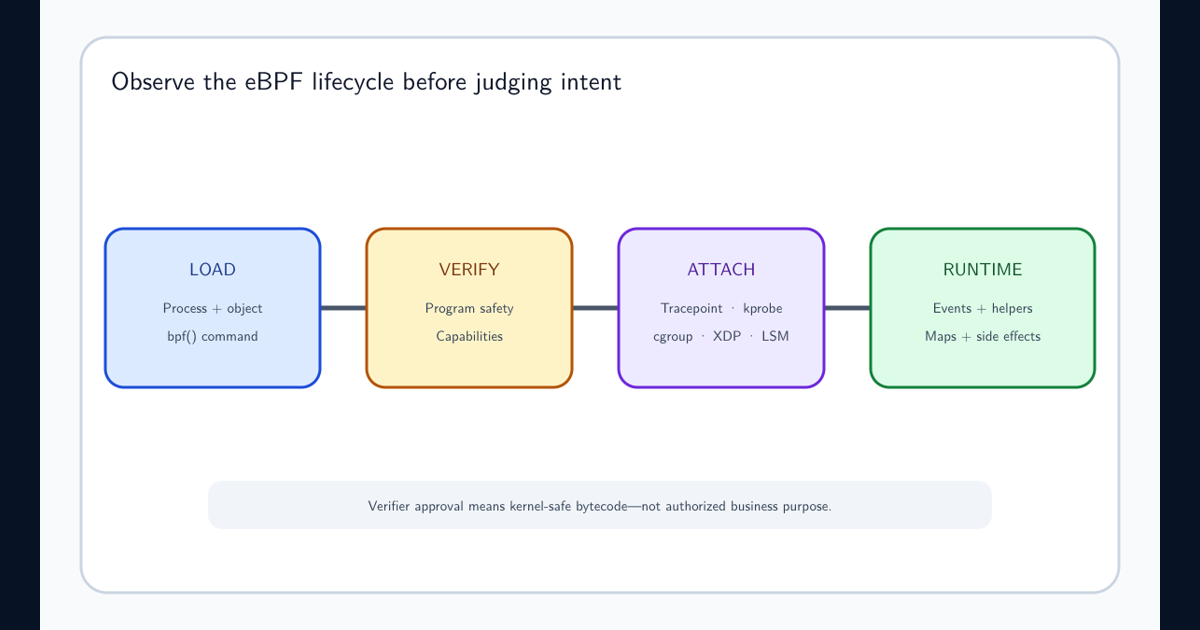
Detect Linux eBPF abuse by inventorying loaded programs, maps, links, loaders, capabilities, attachment points, and resulting endpoint behavior.
A practical top-ten checklist for building endpoint security that prevents common attacks, detects suspicious behavior, supports investigation, and recovers safely.
Protect phones, laptops, tablets, and smart devices through supported software, trusted apps, secure configuration, encryption, and loss preparation.