Endpoint Security
Linux eBPF Abuse: Detection and Hardening
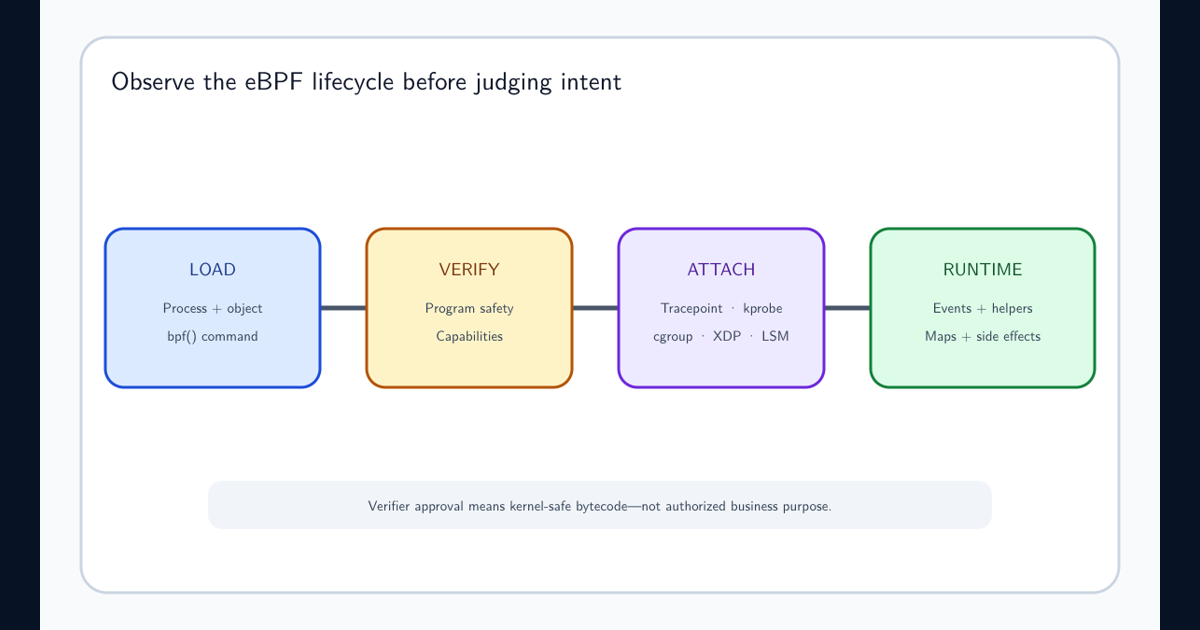
Detect Linux eBPF abuse by inventorying loaded programs, maps, links, loaders, capabilities, attachment points, and resulting endpoint behavior.
Security monitoring and governance for Linux extended Berkeley Packet Filter programs.
1 resource
Detect Linux eBPF abuse by inventorying loaded programs, maps, links, loaders, capabilities, attachment points, and resulting endpoint behavior.